Regulatory context and application milestones
Regulation (EU) 2024/1689, known as the EU AI Act, is the world’s first comprehensive legal framework for artificial intelligence. Its main aim is to manage risks to health, safety and fundamental rights while protecting innovation and the European single market. The full application of its remaining provisions was consolidated on 2 August 2026, the date from which most binding obligations for providers and operators became enforceable.
It is crucial to distinguish immediate prohibitions from transparency obligations that apply in stages. While unacceptable-risk practices have been prohibited from the outset, specific rules for general-purpose AI models (GPAI) and transparency around synthetic content have recently been adjusted through the Digital Omnibus on AI (Regulation (EU) 2026/1744), published in the Official Journal of the EU on 24 July 2026, to simplify implementation without lowering the level of protection.
Legal framework: Article 50 and transparency obligations
Article 50 is the central provision of Title IV of the Regulation and establishes specific obligations for AI systems that interact with people or generate content. Under paragraph 1, providers of systems designed to interact directly with natural persons must ensure users are clearly and unambiguously informed that they are interacting with an AI system. This obligation applies at the system design stage.
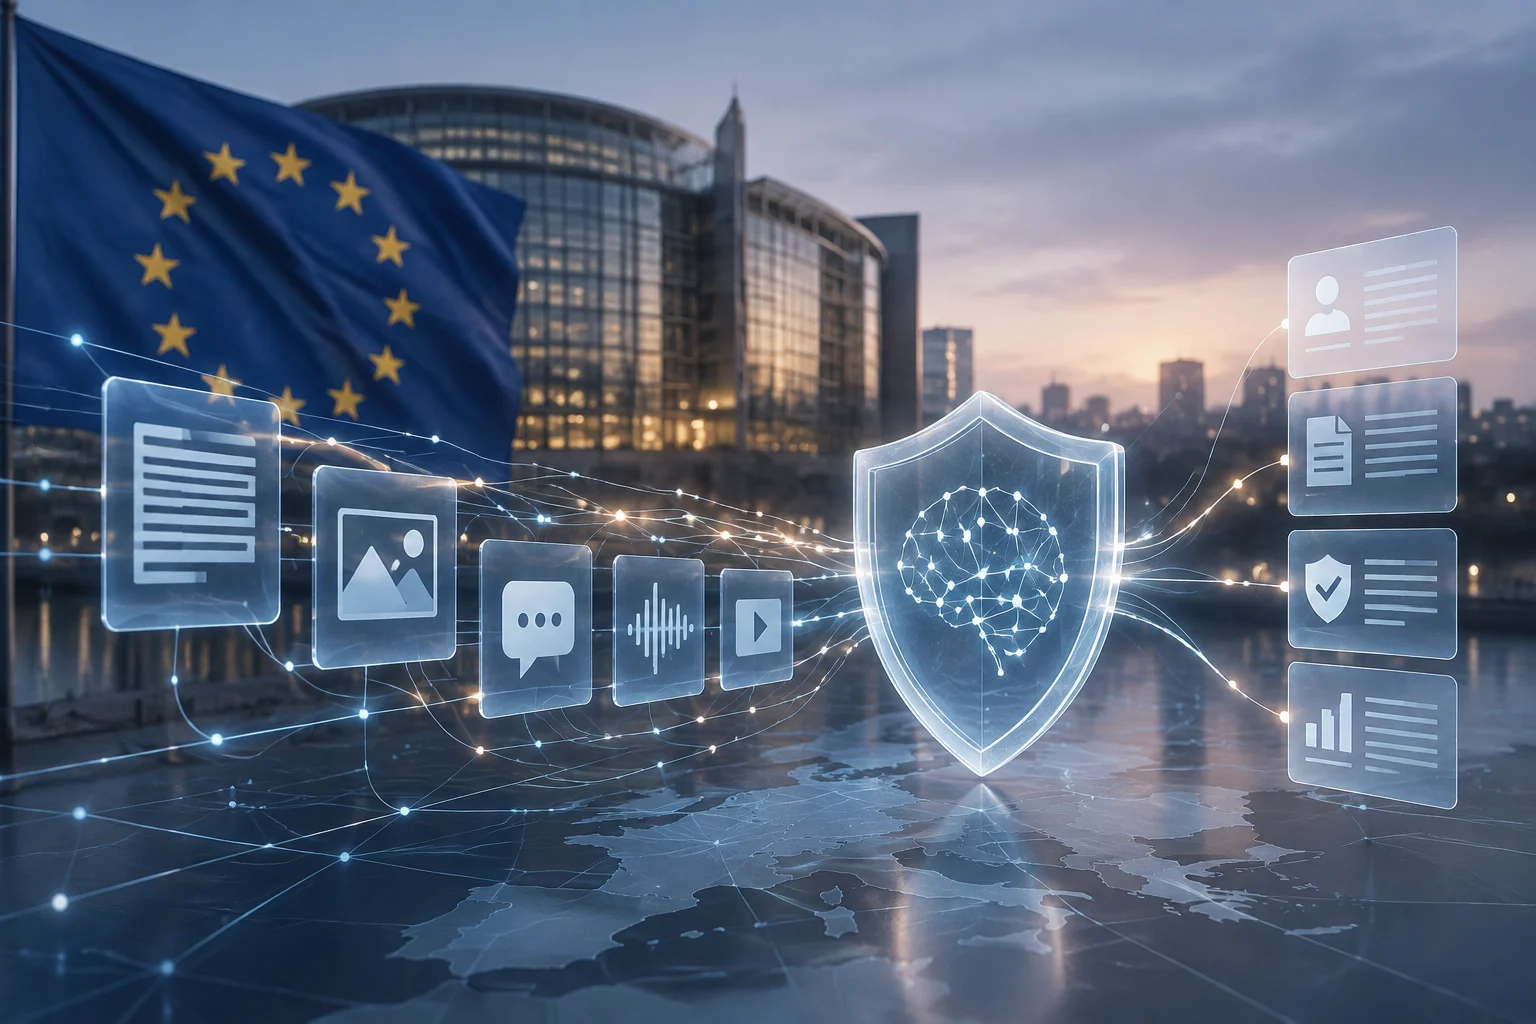
Paragraph 2 imposes a synthetic-content marking obligation on providers of AI systems, including general-purpose systems, that generate audio, images, video or text. Outputs must be marked in a machine-readable format and be detectable as artificially generated or manipulated. This measure aims to mitigate risks of disinformation, manipulation and large-scale fraud, while fostering trust in the digital information ecosystem.
Implementation status among key providers
Implementing these rules requires coordination between the model provider (upstream) and the operator or deployer (downstream). Companies such as OpenAI, Google and Anthropic act as providers under the Regulation and assume obligations independent of those of their corporate customers. The main challenge for companies using these systems lies in the supply chain: many of their compliance duties depend on technical documentation that only the model provider can supply.
In July 2025, the European Commission published the Code of Practice for General-Purpose AI, which is divided into three chapters: Transparency, Copyright and Safety. This code, together with subsequent guidance documents, sets regulatory expectations for GPAI model providers. Adopting the code is one way to demonstrate compliance with transparency and copyright obligations, although it does not exempt providers from direct legal responsibility to national supervisory authorities.
Impact on corporate productivity tools
For IT professionals and compliance leads, the impact means auditing productivity tools that use generative AI, such as writing assistants, data-analysis tools and workflow automation. End users will begin to see practical interface changes, including visible labels for AI-generated content and metadata in exported files indicating their synthetic origin.
Integrating these markers is not merely a legal requirement; it is also an opportunity to improve information governance. Organizations should check that their providers offer technical solutions for machine-readable marking, such as emerging content-credential standards, to ensure their final products comply with the rules when distributed in the European market.
Verification, limits and oversight mechanisms
It is essential to distinguish between what the law requires and companies’ voluntary practices. The Digital Omnibus on AI introduced amendments to address implementation challenges, while leaving the principles of trustworthy, safe and transparent AI intact. Oversight rests with the national authorities designated by each Member State, coordinated by the European Commission’s AI Office.
Companies should be prepared to demonstrate compliance through detailed technical documentation. Under Article 11, for high-risk systems, providers must keep technical documentation up to date, including system architecture, training data and test results. Although Article 50 focuses on transparency, the ability to audit the origin and generation process is key to defending a company’s position in the event of claims or regulatory inspections.
Recommended actions for businesses and users
To adapt to these new rules, organizations should inventory the AI systems they use and check whether their providers have implemented the required labelling measures. They are advised to ask API providers for specific documentation on how they comply with Article 50, including details of the machine-readable marking format and measures for disclosing training data.
Advanced users should become familiar with the new transparency notices in their AI tools’ interfaces. Taking a proactive approach to AI governance not only mitigates legal risks but also positions a company as a responsible participant in the European digital ecosystem, helping build customers’ and business partners’ trust in the integrity of generated content.