What Microsoft announced and why it matters
On October 20, 2026, Microsoft announced new features for Microsoft Sovereign Cloud, its offering for organizations seeking greater control over data handling, system access and the continuity of critical services. The announcement includes capabilities that are available alongside others that are rolling out gradually, are in preview or are planned for later.
The practical change is the ability to choose different models for different workloads. Microsoft describes three options that can be combined: sovereign public cloud, sovereign private cloud and services from local partners. Organizations can assess each system according to its operational and control requirements rather than assuming every application needs the same model.
The offering is aimed, among others, at public administrations and regulated industries. It is not, by itself, a guarantee of regulatory compliance: suitability depends on specific requirements, including data residency, who administers the systems and the continuity conditions that apply to each service.
Three models, without a single architecture
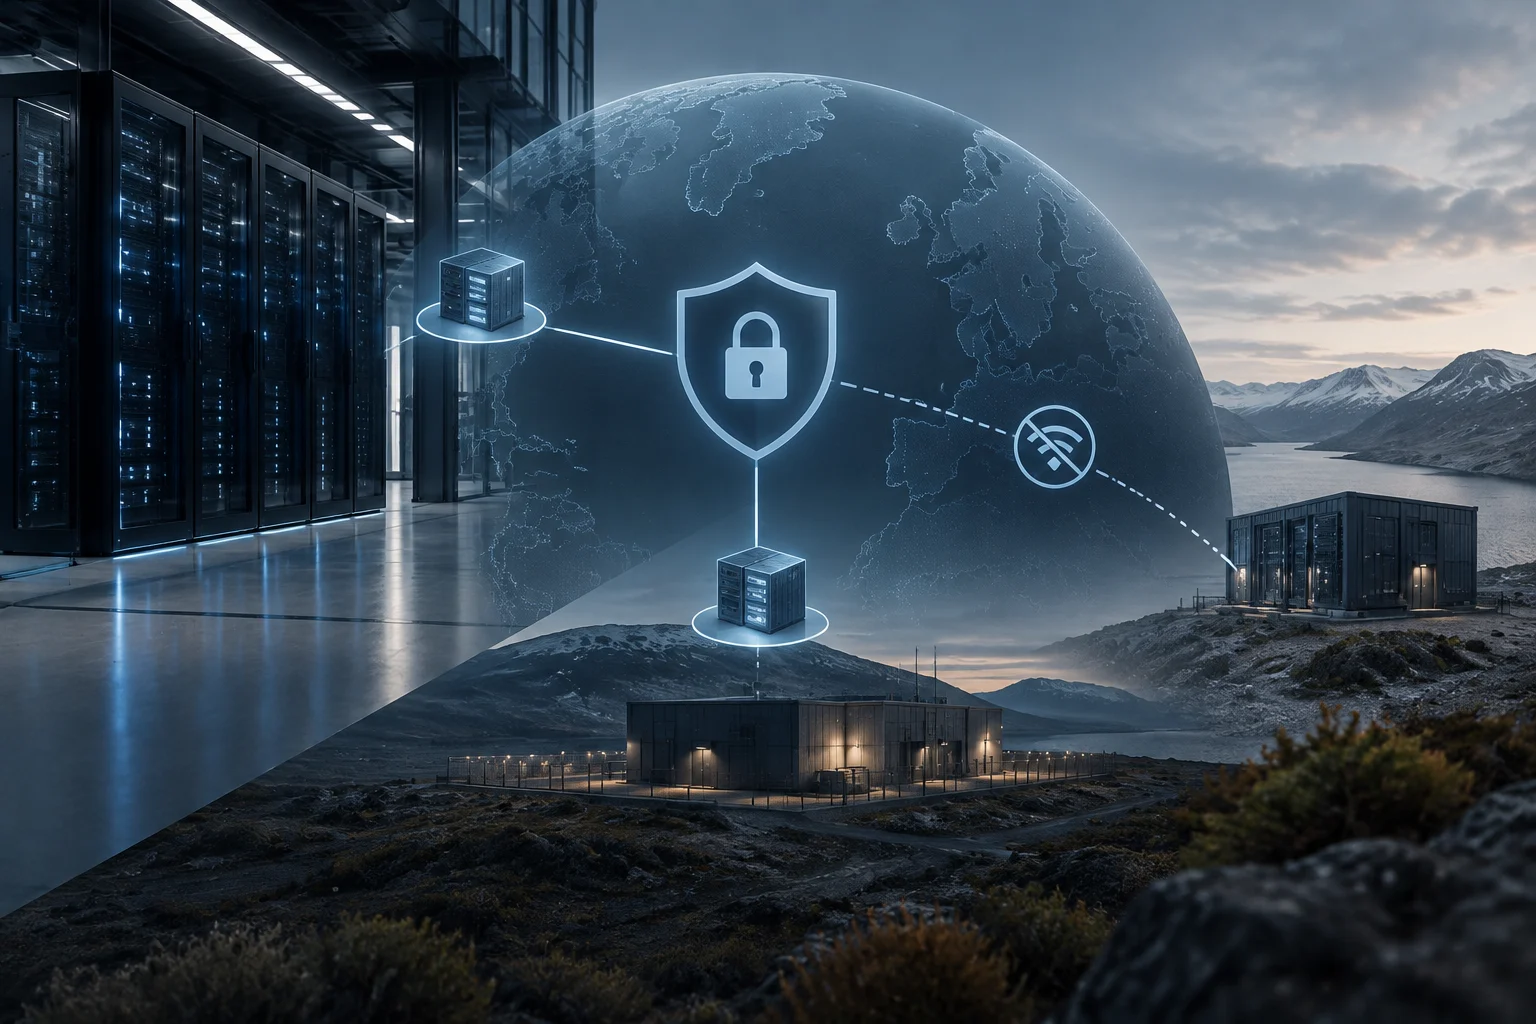
Microsoft presents Sovereign Public Cloud for workloads that require additional controls and transparency within Azure; Sovereign Private Cloud extends services to environments managed by customers themselves, whether connected or disconnected; and the partner ecosystem provides alternatives through independent operators. The company says the models can coexist.
The decision is made workload by workload: data, operational and continuity requirements determine which option may be suitable. Microsoft notes, for example, that some applications may benefit from the scale of public cloud, while others may need to run in facilities controlled by the customer.
These descriptions refer to Microsoft’s offering. To select a configuration, each organization must assess the operating model, access permissions, jurisdiction and contractual terms that apply to its systems.
Access controls, keys and monitoring
Microsoft announced Sovereign Control Panel, a tool that, according to the company, would enter public preview during Microsoft Ignite. Its stated purpose is to bring together information about controls, potential gaps and dependencies between workloads. The announced preview is not general availability.
The company also says it is rolling out Data Guardian to customers in the EU and EFTA, with oversight by a trusted European partner for certain remote engineer access to production systems. Production Touch Ledger, which also began a gradual rollout in those markets, records engineering access and actions. These measures have a defined scope: the announcement does not say that they eliminate all provider access.
Microsoft says External Key Management with Azure Managed HSM is available. This option allows encryption keys to be kept in hardware controlled by the customer or a trusted third party. Its use depends on supported services and on how key management is configured.
Local services and disconnected operation
Sovereign Private Cloud is based on Azure Local, Microsoft’s platform for running cloud capabilities in customer-managed environments. Microsoft’s announcement lists SQL Server on Azure Local as generally available for both connected and disconnected environments. DocumentDB and Blob Storage on Azure Local, by contrast, were announced for a future public preview.
Microsoft also said GitHub Enterprise Local would become generally available during Microsoft Ignite and that GitHub Copilot could use locally hosted models. Foundry Local was announced for general availability on Azure Local during the same event, in both connected and disconnected environments. Availability statuses are not interchangeable: a planned date or preview does not mean a feature is already generally available.
Disconnected operation may be relevant to organizations whose workloads need to function without connectivity. Before considering these options, identify which services are offered in the local environment and their availability status; the announcement distinguishes capabilities already available from those still planned or in preview.
Microsoft Sovereign Cloud: feature status
The announcement describes a mix of available services, gradual rollouts and capabilities planned for Microsoft Ignite or a later public preview.
| SQL Server on Azure Local | Generally available |
|---|---|
| External Key Management | Available |
| Data Guardian | Rolling out in the EU and EFTA |
| Production Touch Ledger | Rolling out in the EU and EFTA |
| Sovereign Control Panel | Public preview planned |
| DocumentDB and Blob Storage | Future public preview |
| GitHub Enterprise Local | General availability planned |
| Foundry Local | General availability planned |
Some rollouts are limited by geography or customer eligibility; announced timing is not a guarantee of general availability.
Sources and references1
What to assess before adopting the features
The announcement identifies alternatives for organizations seeking to combine cloud services with local operations. Selection depends on the requirements of each workload and on the specific capabilities Microsoft includes in each model; there is no single configuration for all customers.
An assessment can begin with specific questions: what data each system processes, who can access it, what residency conditions apply and what needs to happen if connectivity is lost. Organizations should then check whether the required feature is generally available, in preview or only announced, and confirm its geographic scope and contractual terms.
Several announced capabilities depend on gradual rollouts or future dates. Before including them in a migration plan, an organization should confirm the feature’s status and the terms that apply to its configuration and market. Actual availability, not just the cloud category, determines which options can be evaluated now.