What is the Cyber Resilience Act
The Cyber Resilience Act, known as the CRA, is Regulation (EU) 2024/2847. It establishes horizontal cybersecurity requirements for products with digital elements marketed in the European Union. Its goal is to ensure security is part of the product from its design and maintained during the support period, rather than relying solely on the diligence of the buyer.
The regulation addresses two connected problems: products reaching the market with vulnerabilities and manufacturers that do not offer updates or clear information for a sufficient time. To tackle both, it sets obligations throughout the product lifecycle and makes security support more visible. It is not a general company certification nor a law limited to personal data: it regulates product cybersecurity, in addition to the chain of operators that place them on the market.
The CRA has been in force since December 10, 2024, but its obligations apply in stages. Entry into force means the regulation is part of the legal order; it does not mean all requirements are enforceable from that date. General conformity obligations begin on December 11, 2027, while the duty to notify certain incidents and vulnerabilities applies from September 11, 2026.
Which Products Are Covered and Who Is Responsible
The central concept is a product with digital elements: a hardware or software product whose intended purpose or reasonably foreseeable use includes a direct or indirect, physical or logical, data connection with another device or a network. This can include a router, a connected camera, an operating system, a commercial application, or a digital component sold separately. The determining factor is not the commercial label, but the product's functionality and connection.
The regulation assigns responsibilities to manufacturers, importers, and distributors, with the manufacturer as the primary responsible party for designing and maintaining a compliant product. The legal category of manufacturer can extend to a company that markets the product under its own name or brand, or that substantially modifies it. Therefore, a company that buys a finished device and sells it under its own brand should not automatically assume it acts only as a distributor.
Importers must verify, among other things, that the manufacturer has followed the conformity assessment procedure and that the product has the required documentation and marking. Distributors have due diligence duties before marketing and must act on risks or non-compliances they become aware of. In a simple chain, tasks can be summarized as follows, although details depend on each company's legal role:
Responsibilities in the Supply Chain
| Actor | Main Responsibility under the CRA | Practical Meaning |
|---|---|---|
| Manufacturer | Meet essential requirements, assess risks, document conformity, and manage vulnerabilities. | Maintain a security process from development to the end of the support period. |
| Importer | Verify that the product and manufacturer meet applicable obligations before placing it on the EU market. | Review marking, documentation, and required information, and act if risks are detected. |
| Distributor | Exercise due diligence before marketing and cooperate on conformity issues. | Stop offering a product if aware or suspecting a relevant non-compliance. |
| Consumer | Not an operator bound by these marketing obligations. | Benefits from clearer security and support information; the law does not replace safe usage decisions. |
The scope does not mean any digital service is automatically subject to the CRA. The regulation focuses on products with digital elements; certain remote processing services may be relevant when part of a covered product's functionality. There are also exclusions or specific regimes, for example for products covered by specific sectoral legislation and for free software developed outside commercial activity. Do not presume an exclusion just because a product uses open-source code or includes a cloud service: function, distribution, and commercial context matter.
Requirements for Design, Maintenance, and Conformity
The manufacturer must integrate cybersecurity into design, development, and production, assess relevant risks, and adopt proportional measures. Annex I of the regulation includes requirements regarding, among other things, secure default configurations, protection against unauthorized access, and vulnerability management. The practical idea is that security is not added as a last-minute patch: it must influence architecture, development, and market placement decisions.
Vulnerability management continues after sale. The manufacturer must identify and fix vulnerabilities, provide security updates, and declare a support period. This period must consider the product's expected lifetime; the regulation sets a general minimum of five years, unless the product is expected to be used for less time. Five years are not a universal deadline disconnected from the product: the period must be interpreted alongside the expected lifetime and the regulation's conditions.
Before marketing a covered product, the manufacturer must complete the applicable conformity assessment, prepare technical documentation, and issue the corresponding declaration; where applicable, the product will bear the CE marking. The level of assessment depends on classification and available conformity routes. Consequently, the CE marking related to the CRA communicates conformity with applicable requirements, not that the product is invulnerable or will receive indefinite support.
For a company, this turns conformity into a coordinated effort between development, security, product, procurement, and compliance. A product and component inventory helps identify what falls within scope, who holds each role, and what support commitments exist. Maintaining records of risks, changes, updates, and vulnerabilities facilitates responding to both incidents and conformity assessments.
Notification of Vulnerabilities and Incidents
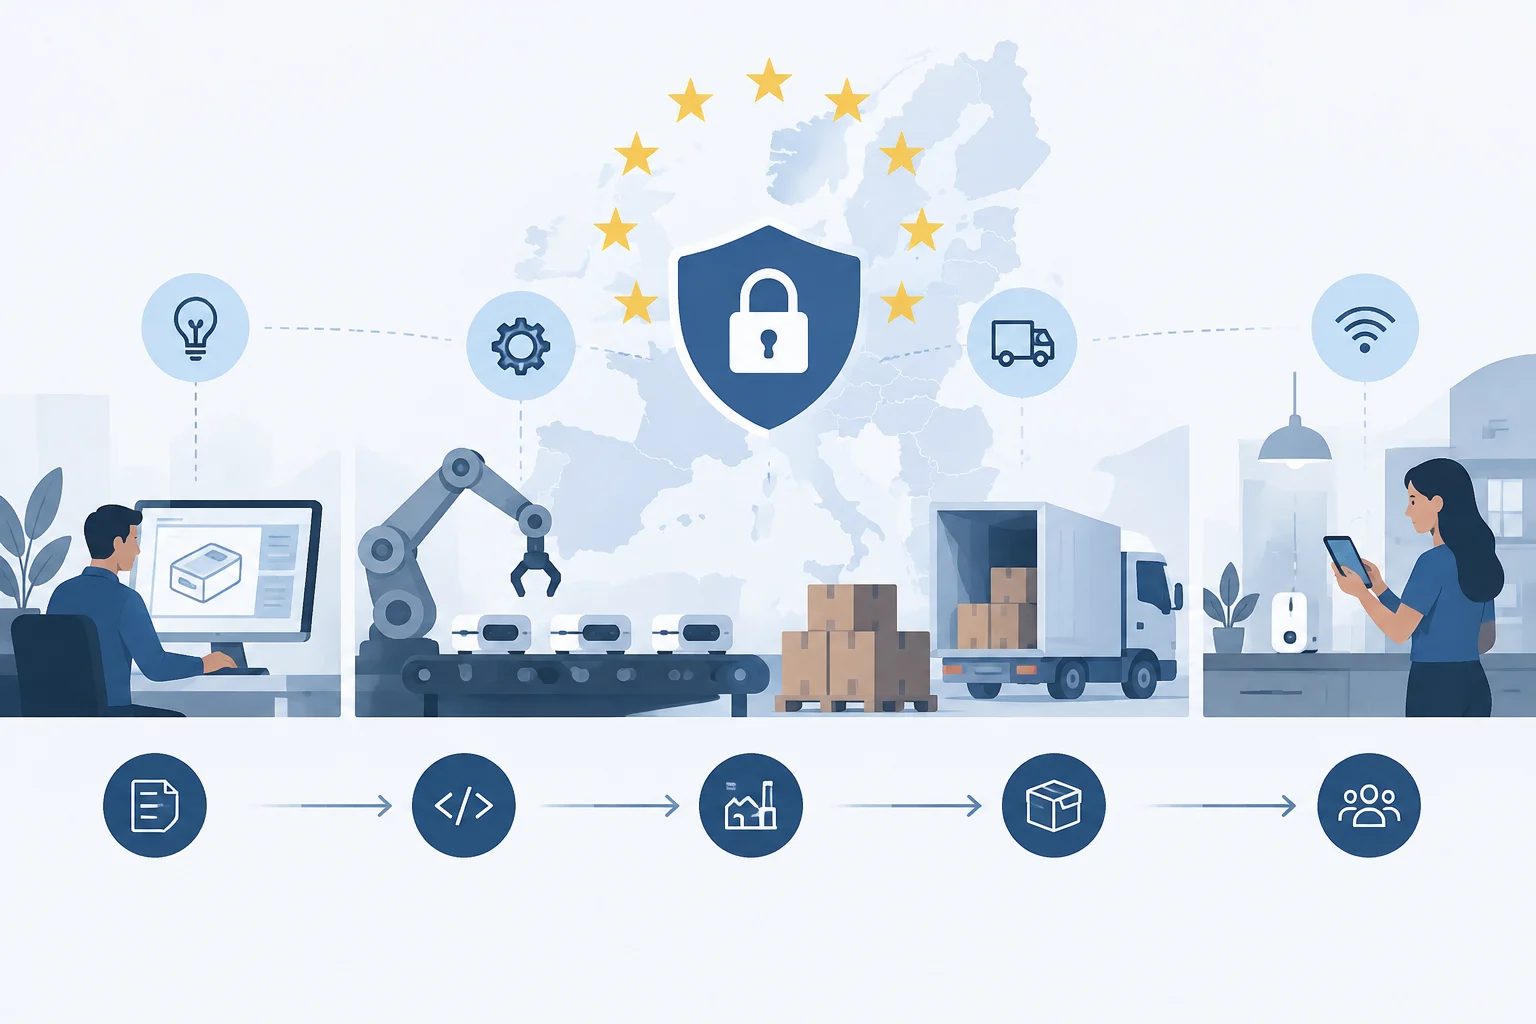
From September 11, 2026, Article 14 requires manufacturers to notify two types of situations: actively exploited vulnerabilities in products with digital elements and serious incidents affecting their security. Not every detected vulnerability becomes a notification of this type: the threshold defined by the regulation must be met. The obligation also covers products already on the market, not just those launched after that date.
Notification follows several stages. The manufacturer must send an early warning without undue delay and, in any case, within 24 hours of becoming aware of the case. Communication is completed within 72 hours. A final report is then submitted: for a vulnerability, within 14 days of a corrective measure being available; for a serious incident, within one month of the 72-hour notification. These are deadlines with different starting points and deliverables, so they should not be reduced to a single deadline.
Notification is channeled through the EU single platform and directed to the corresponding coordinating CSIRT, with simultaneous ENISA access according to the regulation's mechanism. Operationally, the challenge is to quickly recognize if an event affects a covered product, determine when the company has sufficient knowledge, and activate authorized personnel to report. An internal process relying on improvising these decisions after an incident will hardly fit a 24-hour early warning.
Regulatory notification does not replace technical response: investigating scope, containing the problem, preparing an update or mitigation, and informing users when appropriate remain central tasks. Nor does every alert to a national incident response team automatically equal a CRA notification. The criterion is the type of event and the obligation provided in Article 14.
Timeline: Entry into Force and Application
The timeline has three milestones to distinguish. The regulation entered into force on December 10, 2024. Obligations to notify actively exploited vulnerabilities and serious incidents apply from September 11, 2026. General application of the remaining main obligations is scheduled for December 11, 2027.
| Date | What Happens | Practical Consequence |
|---|---|---|
| December 10, 2024 | Entry into force of Regulation (EU) 2024/2847. | The law exists legally, but most obligations still have a transitional period. |
| September 11, 2026 | Article 14 notification obligations apply. | Manufacturers must be able to notify prescribed cases, even if affecting already marketed products. |
| December 11, 2027 | General application of main obligations. | Cybersecurity, conformity, and documentation requirements apply to covered products. |
The effect of dates on a specific product depends on its situation and the transitional regime. A company should not interpret 2027 as permission to delay all preparation: notifications are already enforceable from September 2026, and design, support, and assessment processes need time. At the same time, saying the CRA fully applies from 2024 would be incorrect: the timeline is phased and each obligation must be associated with its own milestone.
To organize work, an initial review can follow this order: identify products sold in the EU; determine if each falls within scope; assign manufacturer, importer, or distributor; review vulnerabilities and notification processes; and plan conformity assessment, documentation, and support for the 2027 general milestone. Classification and exceptions require case-by-case analysis, not a single rule for all categories.
Difference Between the CRA and the GDPR
The CRA sets cybersecurity requirements for products with digital elements and obligations for economic operators marketing them. It is designed to address product security across the product lifecycle, including vulnerabilities and security updates.
For consumers comparing devices, it can be useful to check who provides security updates, how long support is expected to last, and what the manufacturer says about support. The CRA aims to improve the transparency of this information, but it does not guarantee that intrusions will never occur or that a product has no defects.
The CRA seeks to strengthen product security and make support information clearer. When comparing devices, check who offers updates, how long support is expected to last, and what information the manufacturer provides. These details can help you understand the product’s expected maintenance.