What DNS over HTTPS is
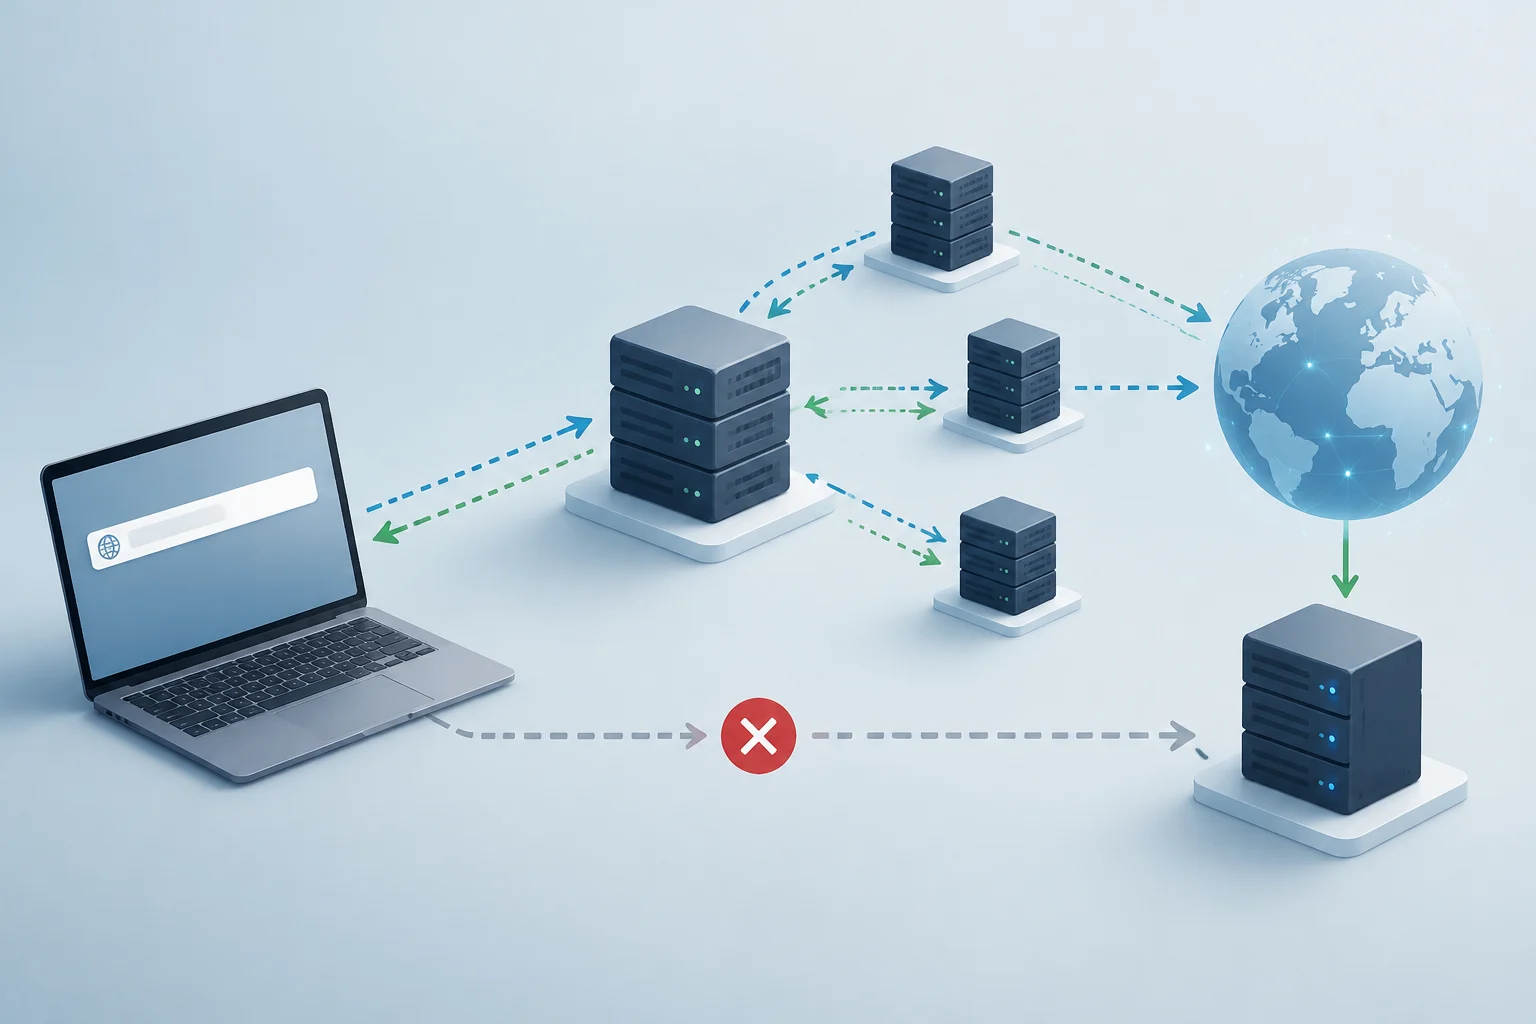
DNS over HTTPS (DoH) is a protocol for sending DNS queries and receiving responses using HTTPS. RFC 8484 maps each DNS query-and-response exchange to an HTTP exchange. By using HTTPS URIs, the protocol employs TLS to protect the integrity and confidentiality of that communication.
RFC 8484 was published in October 2018 and addresses communication between DNS clients and recursive resolvers. Goals considered during its development included making interference by devices on the network path more difficult and allowing web applications to access DNS information through browser mechanisms. Its scope is DNS transport, not the privacy of all online activity.
DoH integrates with HTTP features such as content negotiation, caching, redirection, proxies, and authentication. The fact that the protocol supports these features does not mean that every service or configuration uses them in the same way; their behavior depends on the implementation and the service.
How queries are transported
Each DNS query is encoded in an HTTP request, and the response arrives in the corresponding HTTP response. RFC 8484 provides for the GET and POST methods: with GET, the query is included in the URI as the dns variable, encoded using base64url; with POST, it is sent directly in the request body.
The content type defined for messages is application/dns-message. The specification requires the HTTPS scheme and describes TLS as providing integrity and confidentiality protection. That protection applies to the exchange between the client and the DoH server; it does not justify claiming that all risks of tracking or traffic analysis disappear.
The client must have the DoH server URI configured. RFC 8484 states that this configuration is performed outside the protocol and may be manual or automatic. Therefore, DoH does not select a provider by itself or establish what data policy applies: those matters depend on the configuration and the service selected.
What it protects and what it does not guarantee
According to the RFC, DoH encrypts DNS traffic and requires server authentication. This mitigates passive surveillance and certain active attacks that try to divert queries to fraudulent servers. The protection applies to the path between the client and server, not to every communication generated by an application.
Encryption along that path is not the same as anonymity. The RFC warns that HTTPS may include data useful for correlating requests, such as explicit HTTP cookies and header characteristics. In addition, the DoH server processes the queries it receives; the protocol does not establish what a particular provider retains or what privacy policy it follows.
DoH also does not, by definition, encrypt all browsing content. The RFC defines the transport of DNS queries and responses over HTTPS, not an end-to-end connection for the rest of the traffic. It should therefore not be described as a substitute for a VPN or as a guarantee that the user’s IP address is hidden.
Choosing a DoH server
The choice of server matters because the client sends the queries it needs to resolve to that server. RFC 8484 specifies that the client uses a configured URI to select the server, while configuration, discovery, and updates are outside the protocol. The standard does not prescribe a provider or how that provider handles data.
Before choosing a service, review who operates it and what information it publishes about query processing. The RFC explains how the client communicates with the server, but it does not establish how long each provider retains data, who can access it, or what terms apply.
The network context may also matter. If internal names or policies managed by an organization are in use, check with the network administrator to confirm the appropriate configuration. The protocol specification does not set a universal recommendation for corporate, educational, or public networks.
Firefox: configuration and limits of the available information
The Mozilla documentation supplied for DNS over HTTPS does not provide usable information here about the Firefox interface. As a result, current option names, menu paths, available providers, and step-by-step configuration instructions cannot be substantiated.
RFC 8484 does make it possible to describe the general requirement: the client needs a configured server URI, set manually or automatically outside the protocol. That does not establish how Firefox implements it or show which options appear in a particular version.
To change the browser configuration, consult the official Mozilla help for the version you use and check the options shown there. Do not assume that menu paths or provider lists from unconfirmed instructions are current: the RFC describes DoH, not a browser’s interface or specific decisions.
Exceptions, errors, and practical decisions
RFC 8484 defines how DNS messages are exchanged over HTTP, but it does not document Firefox’s protection levels, domain exceptions, defaults, or when it falls back to another resolution mechanism. Those aspects belong to the browser implementation and should not be inferred from the rules for GET, POST, or TLS.
The standard does cover HTTP responses and DNS errors, but that does not establish what a specific Firefox version will do when a server does not respond. Nor does it specify how the browser handles internal network names or the conditions it uses to switch mechanisms. Current product documentation is needed for those details.
As a practical guide, separate three questions: what the protocol protects, what options the browser offers, and what practices the provider declares. The RFC addresses the first; current Mozilla help addresses the second; and the privacy information published by the selected service addresses the third. None automatically answers the others.
When DoH may be appropriate
DoH may be relevant if you want to protect communication of DNS queries between a client and a resolver using HTTPS. The RFC identifies reducing interference by devices on the network path as a motivation, but it does not promise to solve every privacy problem or ensure that every network and client behaves in the same way.
Before enabling it, identify which server the browser selects and review the privacy practices published by that service. If you rely on internal names or policies for a managed network, check with its administrator about the configuration you should use rather than assuming that a generic option will be suitable.
The conclusion is limited: DoH protects the transport of DNS queries as defined by the protocol. Browser configuration, the chosen server, and the rest of the connection are separate matters. DoH is not equivalent to anonymity, end-to-end encryption of browsing, or a VPN; for specific instructions, consult current browser documentation.