The Digital Regulatory Ecosystem in 2026
The European Union has consolidated a digital regulatory framework that no longer limits itself to data protection, but encompasses product cybersecurity, platform responsibility, and artificial intelligence governance. In 2026, these norms cease to be future proposals and become enforceable obligations with specific deadlines and million-euro fines.
The impact is cross-cutting: it affects hardware and software manufacturers, online service providers, companies deploying AI systems, and ultimately end users. The key to navigating this ecosystem is distinguishing between what is already current law and what is in a transition phase or has been subject to recent regulatory adjustments.
GDPR and ePrivacy: The Consolidated Foundation
The General Data Protection Regulation (GDPR) remains the fundamental pillar of privacy in Europe. Although its full application dates back to 2018, its interpretation and application evolve constantly. The European Data Protection Board (EDPB) published its annual report in 2024, highlighting the adoption of a new 2024-2027 strategy to reinforce the consistent application of the GDPR in a changing digital landscape.
The EDPB strategy focuses on inter-regulatory cooperation, recognizing that data protection does not operate in a vacuum but interacts with other regulations such as the AI Act or the CRA. For companies, this means that GDPR compliance must be integrated with new transparency and security obligations, avoiding regulatory silos and ensuring unified digital risk management.
Digital Services Act (DSA): Platforms Under the Microscope
The DSA (EU Regulation 2022/2065) entered into force on February 17, 2024, and regulates the responsibility of digital intermediaries, online platforms, and search engines. Its application is phased: general obligations apply from 2024, while very large platforms (VLOPs and VLOSEs) have specific deadlines to comply with additional requirements for systemic risk assessment.
In September 2026, the European Commission designated new services as VLOPs and VLOSEs, including ChatGPT (as a VLOSE), Reddit, and Roblox (as VLOPs). These services have four months, i.e., until January 2027, to comply with additional obligations, including mitigating risks related to the spread of illegal content, protecting minors, and user well-being. In Spain, the CNMC acts as the Digital Services Coordinator, supervising compliance and managing complaints.
Digital Markets Act (DMA): Controlling 'Gatekeepers'
The DMA complements the DSA by focusing on competition and fairness in digital markets. It establishes specific obligations for 'gatekeeper' companies that control critical access points to digital markets. DMA compliance has led to the imposition of significant fines, such as the 120 million euro fine on X (formerly Twitter) for non-compliance in its platform design.
The DMA seeks to prevent anti-competitive practices and ensure that users and companies have real choices in the digital ecosystem. For tech companies, this implies a deep review of their business models, interfaces, and interoperability practices. Active supervision by the European Commission and national coordinators, such as the CNMC, ensures that the rules do not remain on paper but translate into tangible changes in user experience.
CRA and AI Act: The New Fronts of 2026
The Cyber Resilience Act (CRA, EU 2024/2847) is the first EU regulation establishing mandatory cybersecurity requirements for products with digital elements throughout their lifecycle. From September 11, 2026, the obligations to notify vulnerabilities and serious incidents provided for in Article 14 are fully enforceable. Full application of the CRA, including conformity assessment and CE marking, will extend until December 11, 2027.
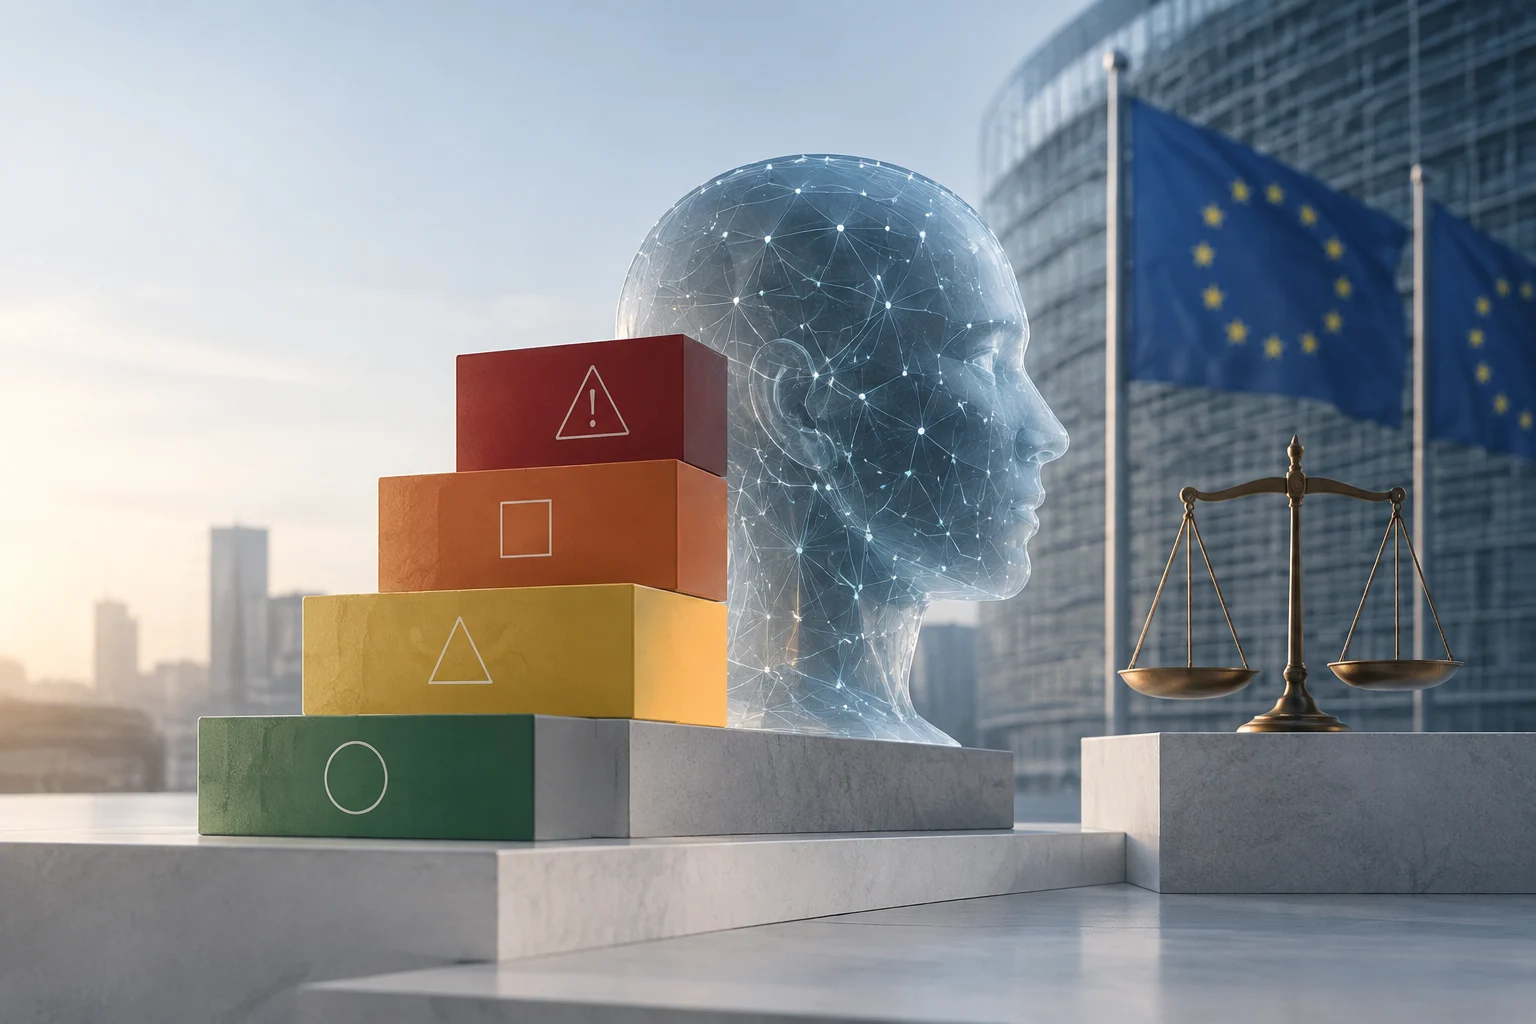
In parallel, the AI Act entered into force on August 1, 2024, with phased application. Prohibitions and AI literacy apply from February 2025. However, in May 2026, European institutions reached an agreement to postpone the most demanding obligations for high-risk systems until December 2, 2027, as part of the Digital Omnibus package. This postponement aims to reduce the administrative burden for SMEs and allow the publication of official technical guidelines, although transparency obligations for general-purpose models and deepfakes remain in force from August 2026.
How to Verify Compliance and Official Resources
For companies, the first step is to conduct an inventory of products, services, and AI systems operating in the EU. Next, they must map each asset against the specific obligations of the DSA, DMA, CRA, and AI Act. It is crucial to identify whether they are classified as VLOP/VLOSE, gatekeeper, manufacturer of products with digital elements, or AI provider/deployer.
Official resources, such as the European Commission pages (digital-strategy.ec.europa.eu) and national coordinators (CNMC in Spain), offer guides, complaint forms, and regulatory updates. Companies must keep up to date with regulatory changes, especially those derived from the Digital Omnibus package, which continues to reconfigure the European digital economy. Early preparation not only avoids fines but positions organizations as leaders in digital trust and regulatory compliance.