Technical definition: Generative AI vs. action agents
The fundamental distinction between a chatbot and an agent lies in the ability to execute external actions. Generative AI focuses on creating new content, such as texts or images, based on previous data patterns, while an advanced AI assistant can understand natural language and complete tasks ranging from answering questions to executing multi-step workflows.
In a business context, an AI assistant is a software application that uses natural language processing and machine learning to understand requests and perform specific tasks. Unlike rudimentary chatbots that followed decision trees, modern agents possess memory, tools, and permissions to act on external systems, such as querying inventories or creating order drafts.
This evolution implies that the line between text generation and state modification in databases has become blurred. For the end user, the interface may appear identical, but the underlying architecture determines whether the system only suggests or actually modifies data in real time through API integrations.
Step 1: Inspect 'Action' and 'Tool Use' documentation
The first technical indicator is the presence of tool use capabilities or custom actions in the provider's documentation. Platforms like Salesforce Agentforce allow connecting automation flows through specific actions, demonstrating that the agent does not just converse but invokes predefined logical processes.
You must look for sections in the documentation that describe how the assistant interacts with external APIs. If the system uses protocols like MCP (Model Context Protocol), this indicates an architecture designed to expose data and functions as invocable tools. For example, an MCP server can allow an assistant to query products and prices, but the documentation must clearly specify if those permissions are read-only or include write capabilities.
The absence of documentation on executable actions suggests that the assistant operates in a pure generation mode. Conversely, the presence of data schemas for tool input and output confirms that the system is designed to interact with external environments beyond the chat.
Step 2: Audit integration permissions and access tokens
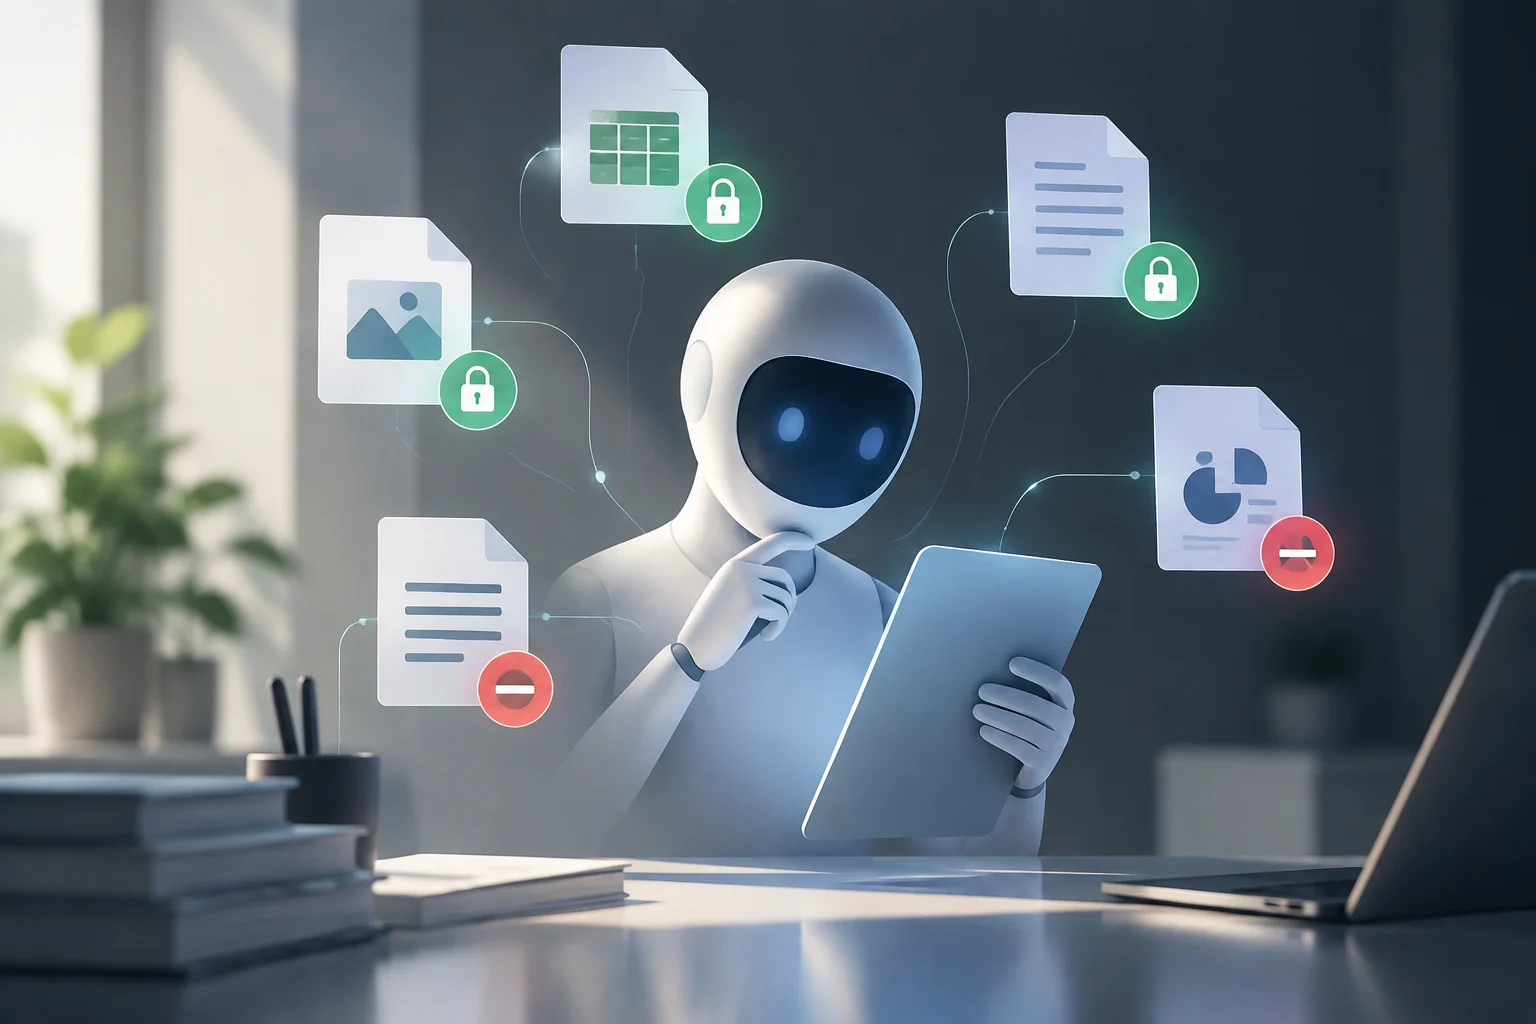
Permission verification is critical to determine the actual scope of actions. In integrations with systems like SAP Business One, the agent translates user requests into API operations, which requires access tokens with specific privilege levels. It is fundamental to review if these tokens grant read-only rights or allow the creation and modification of records.
A secure architecture usually implements granular permissions. For example, in trading or finance environments, it is recommended to grant read-only permissions for data queries and reserve write permissions for human confirmation flows. If an office assistant has access to a token with write permissions in your CRM or ERP, you must assume it can modify data without your direct intervention.
Review the OAuth configuration or API keys in the admin panel. Verify which scopes are active. An assistant that only generates email drafts does not need automatic sending permissions; if it possesses those permissions, the boundary between suggestion and execution has been crossed.
Step 3: Verify the existence of audit logs
Traceability is the hallmark of a mature production agent. An assistant that executes real actions must leave a detailed audit log of each operation performed. This includes the time, the user who requested the action, the tool invoked, and the result of the operation in the destination system.
In enterprise platforms, AI agent auditing allows tracking usage and decisions made. Without this record, it is impossible to determine if a database modification was made by a human or by the assistant. The lack of logs is a red flag indicating a lack of governance and control over automated actions.
Logs must be immutable and accessible to security administrators. In advanced agentic architectures, each action is auditable and reversible, allowing human supervisors to revert changes if the agent acts outside expected parameters. This reversal capability is a key component of operational security.
Step 4: Perform controlled tests with reversible actions
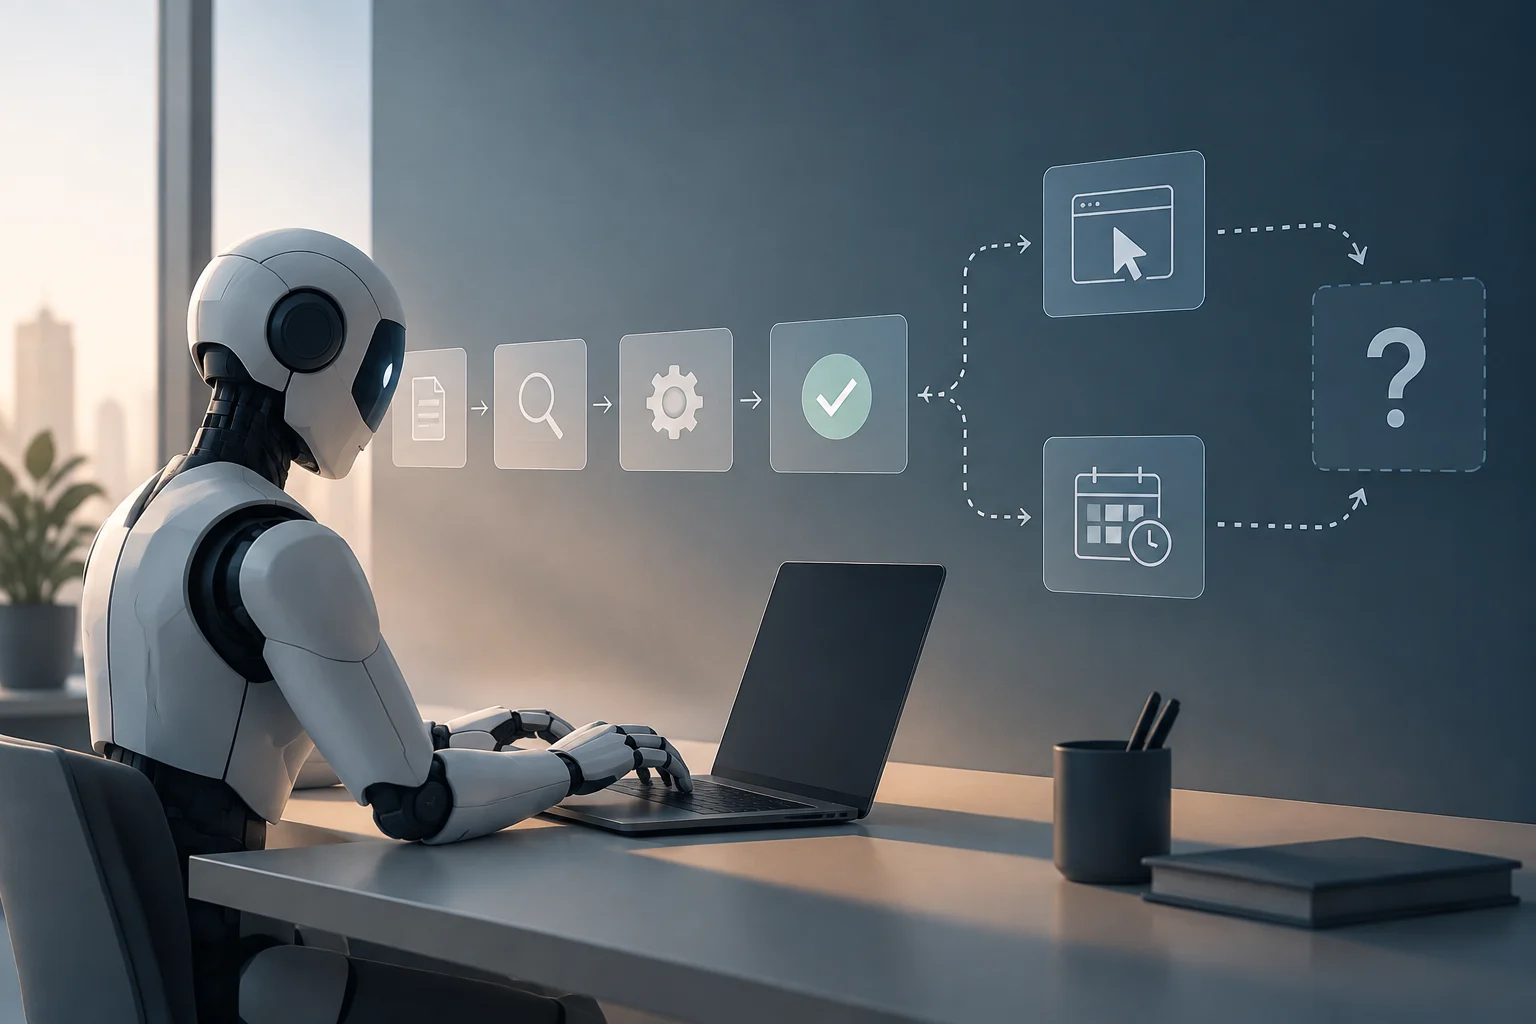
The definitive test is the controlled execution of a low-risk task. Select a reversible action, such as creating a calendar event or generating an email draft, and observe if the assistant completes it without manual intervention. If the event appears in your calendar with the correct details, the assistant has executed a real action through an API.
During this test, verify latency and confirmation. An agent that executes actions usually provides explicit confirmation of the operation performed, while a text generator will only offer a conversational response. If the assistant asks for confirmation before executing, this indicates a confirm-to-trade or similar architecture, designed to mitigate risks.
Document the test result. If the action is executed and is reversible, you can trust the assistant's operational capability for routine tasks. If the action fails or the assistant only generates the request text without executing it, you must reconfigure usage expectations towards content generation and not towards process automation.
Criteria for deciding suitability in critical tasks
Based on the inspection of documentation, permissions, and auditing, you can classify the assistant into two categories: content generator or action agent. Generators are suitable for drafts, summaries, and text analysis, but should not be granted write permissions in critical systems.
Action agents, which have demonstrated execution capability and traceability, can assume more complex tasks such as inventory management or staff scheduling. However, even in these cases, it is recommended to maintain human supervision for high-impact decisions, such as credit approval or price modification.
The security of an AI assistant in production depends on the separation between instructions and data, and the ability to audit each interaction. Implementing confirmation flows and read-only permissions for non-critical functions reduces the risk of chain errors and protects the integrity of business data.