The difference lies in actions, not labels
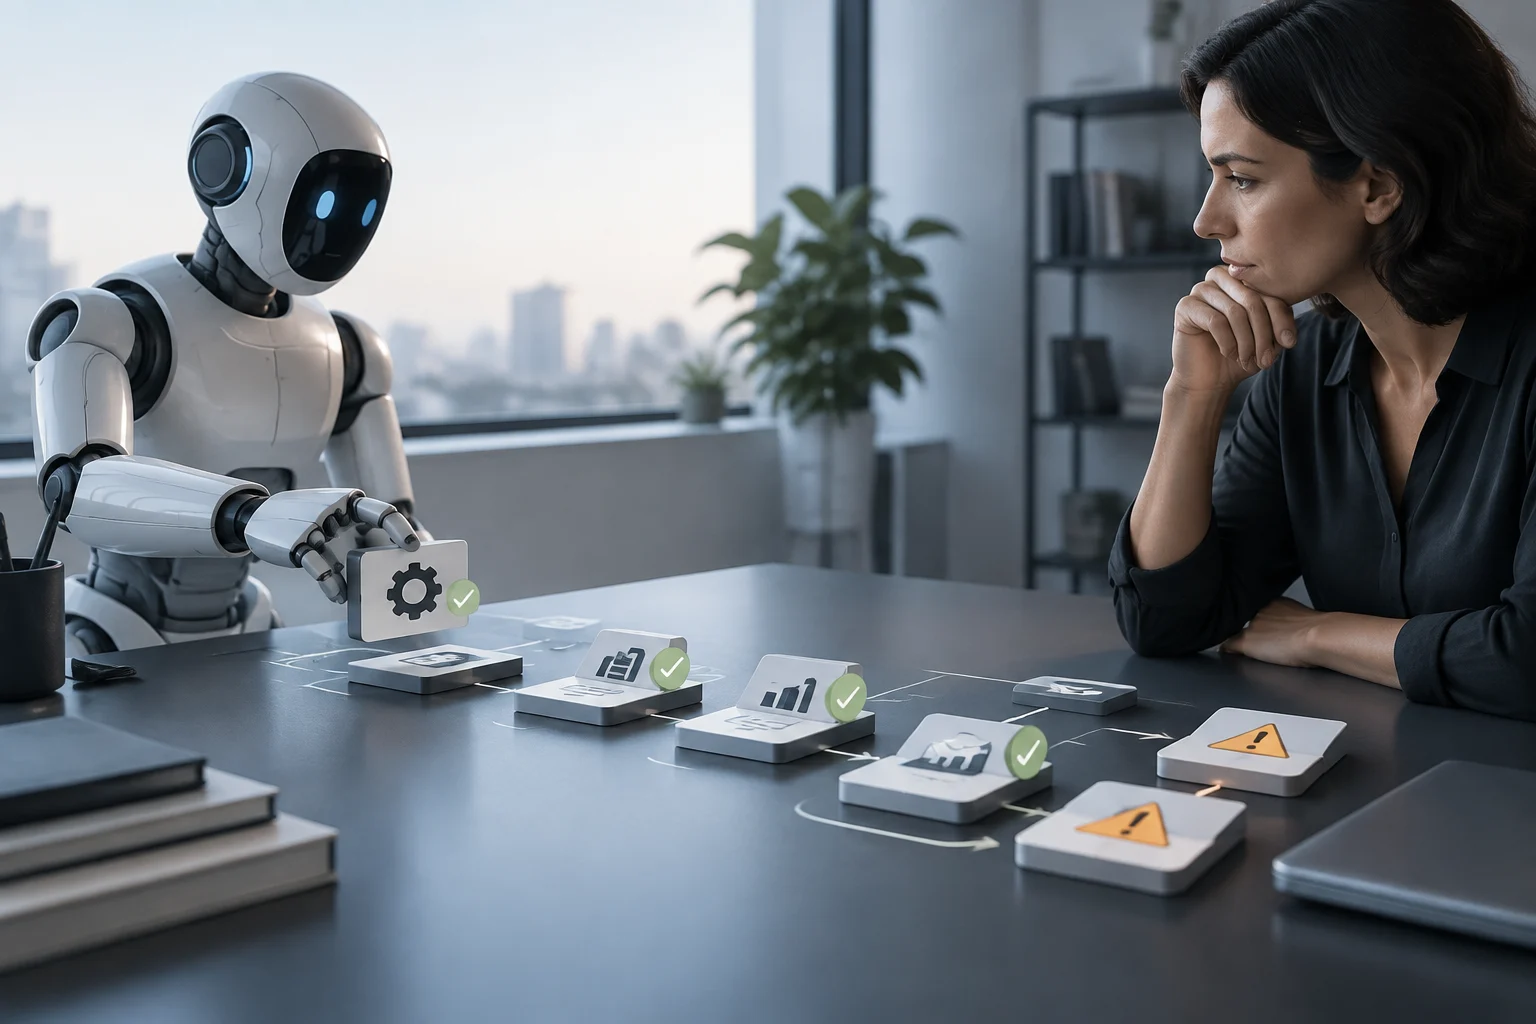
A conversational assistant receives an instruction and returns text; an agent can additionally invoke tools, modify resources, or chain steps to achieve a goal. The practical signal of autonomy is that the system can act, not that the model reasons extensively or writes a lengthy response.
The distinction matters because reasoning and executing are separate capabilities. A model can plan a complex task without touching the device; to interact with files, an application, or the network, it needs specific tools and permissions. Do not infer system access from the name “AI” or “agent”: check which tool is connected and what authorizations it received.
It is also worth clarifying the scope of this guide: Android Studio is a development environment, not the general permissions panel for Gemini Nano on Android 16. Google’s documentation on agent permissions describes the operations available to the Android Studio agent, such as editing project files, using domains, executing shell commands, and connecting MCP servers. Those controls do not demonstrate what Gemini can do on the phone.
Windows 11: checking if the feature is present
A Microsoft training module describes the evolution of Windows towards integrated agents and notes that some experiences, such as the agent workspace, are in preview and subject to change. That description does not confirm that a feature is enabled on every PC.
To check an agent in Android Studio, open File > Settings > Tools > AI > Agent Permissions; on macOS, use Android Studio > Settings > Tools > AI > Agent Permissions. The panel lets you review the agent’s permissions for actions such as reading or updating project files, accessing domains, running shell commands, and interacting with MCP servers. Check the scope of each permission before approving it.
Technological coverage published in December 2025 described a proposal for individual permissions for agents and personal folders in Windows 11. It included options such as allow, ask, or deny and highlighted differences between folder permissions. It is a secondary report on a feature in development, not a universal guarantee of current behavior or an instruction to find that menu in any installation.
Android: separating the operating system from Android Studio
On an Android mobile device, application permissions are reviewed from the device’s own controls—for example, the permissions manager for camera, microphone, location, and contacts—and within the options of the corresponding application. Names and paths may vary by manufacturer and version. An app’s permission is not equivalent to a global authorization for all agents.
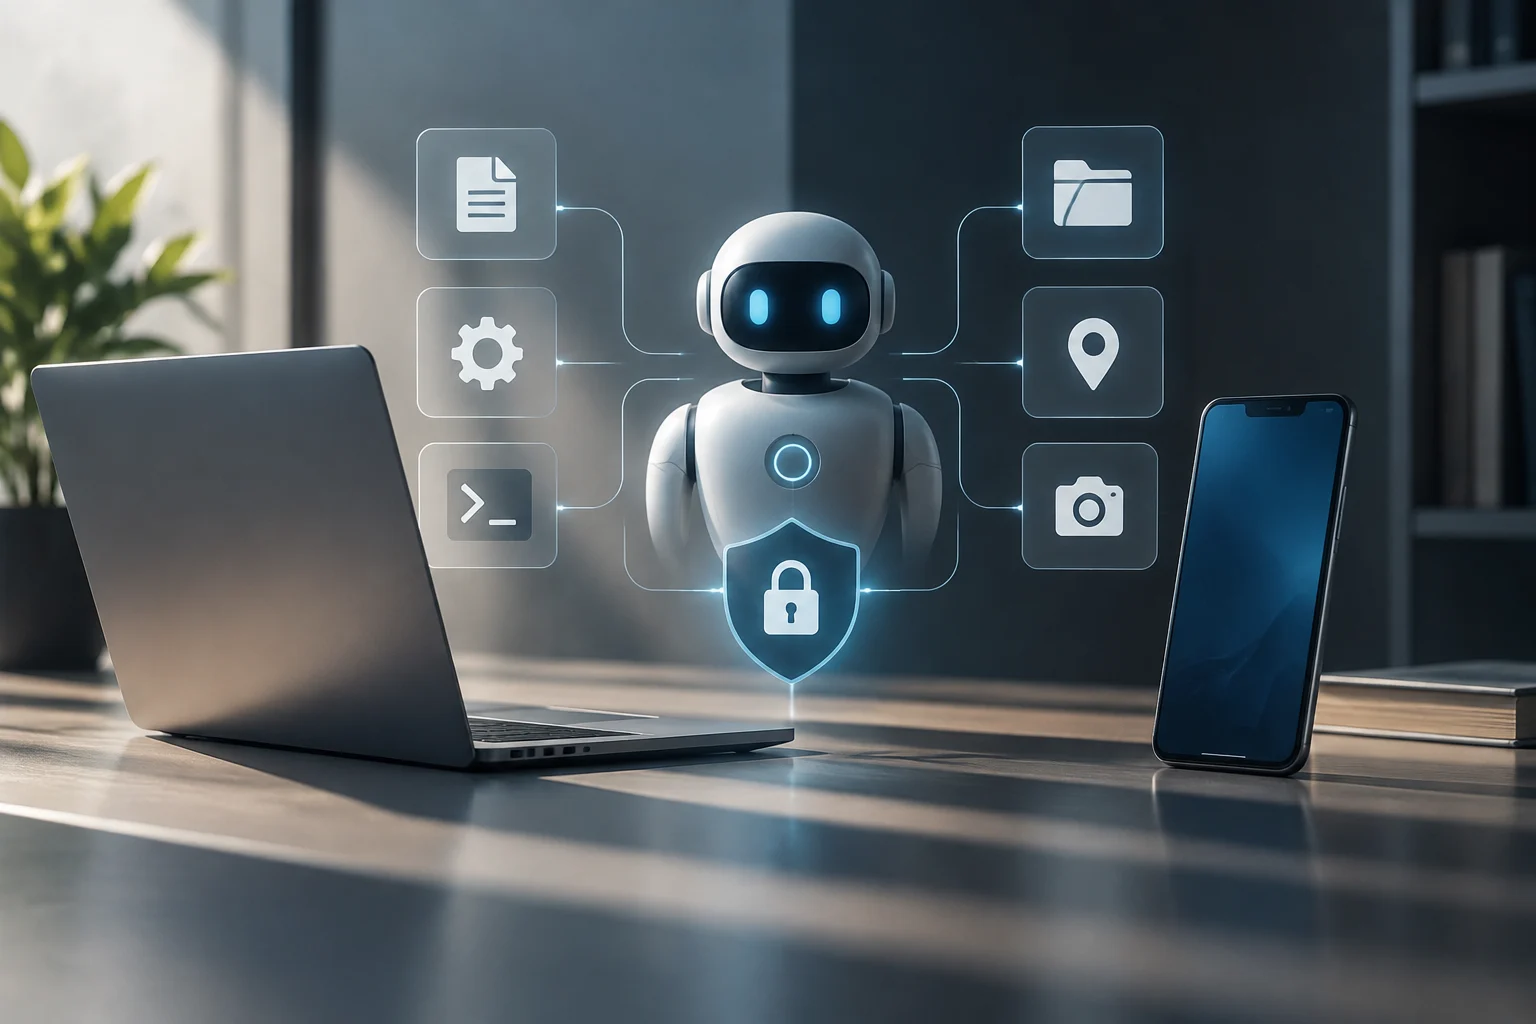
Google’s documentation on Agent Permissions refers specifically to the Gemini agent in Android Studio. It lists authorizations to read and update project files, access Google Search and other domains, execute shell commands, and interact with MCP servers. The user can approve a single operation or allow it persistently, and the guide explains that certain high-level permissions can enable related tools. This serves to audit a development environment, not to measure Gemini Nano’s access on Android 16.
In Android Studio, the documented path to review these permissions is File > Settings > Tools > AI > Agent Permissions; on macOS, Android Studio > Settings > Tools > AI > Agent Permissions. The same guide offers an Agent Shell Sandbox option to limit network access and file system writes unless authorized. Review the scope of the permission before accepting: granting write access to a project should not be interpreted as general permission over the entire phone.
A practical method to limit scope
The most reliable review starts with the resource and the action, not with a generic privacy promise. For each agent, note which files it can read or modify, which domains it can contact, whether it can execute commands, and whether it interacts with other applications. Request the minimum permission that allows completing the task and choose single authorization when it is not a repeated and reliable flow.
In Android Studio, review permissions under File > Settings > Tools > AI > Agent Permissions; on macOS, use Android Studio > Settings > Tools > AI > Agent Permissions. The Agent Shell Sandbox setting can limit network access and file-system writes unless you explicitly authorize them. Review the scope of a permission before accepting it.
Before allowing a risky action, confirm its effect: which file will change, which command will be executed, or which service it will connect to. For significant changes, require human confirmation and keep a recoverable copy of the data. If the agent works with sensitive information, test first with non-critical data and check if the operation requires a connection to a remote service.
Real risks and limits of permission-based control
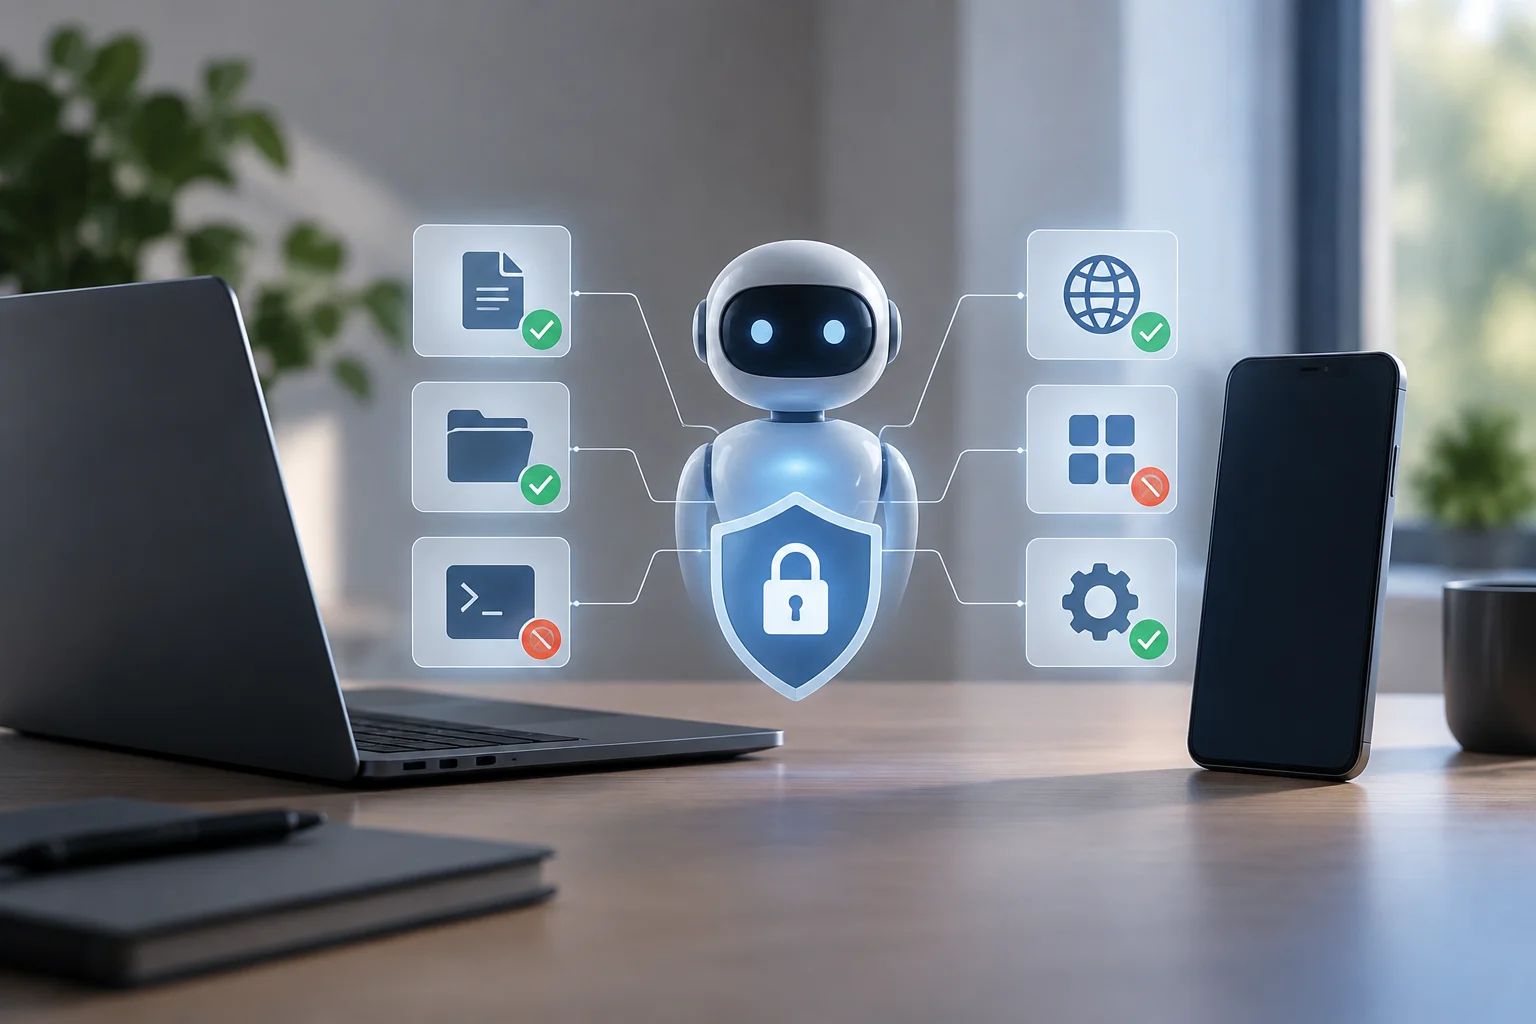
File access can expose documents or credentials; write access adds the risk of unwanted changes. Shell commands and network connections expand the potential impact because they can affect the work environment or send information to external services. Reading, modifying, executing, and transmitting are distinct permissions and should be evaluated separately.
A consent screen reduces unauthorized actions but does not prove that a task is safe or that the result is correct. The Android Studio guide, for example, describes single and persistent approvals and permissions that group related tools. A broad authorization can cover more than one operation; the person must review its scope and maintain supervision over sensitive actions.
It is also necessary to differentiate local and remote processing. The fact that a model or agent uses AI features does not, by itself, allow concluding where each request is processed or what data is sent. That information depends on the specific application and service; check its settings and data policy before introducing confidential content.
Periodic checklist
A monthly review can focus on observable changes, without assuming that all systems offer the same inventory. Check if you installed new agents, if an application added tools, or if you granted persistent permissions you no longer need. Revoking an unnecessary authorization reduces future access, although it does not undo previous actions.
Use this brief list when installing an agent, changing versions, or working with sensitive data:
- Identify the exact application, agent, and platform; confirm whether it is Windows, Android, or Android Studio.
- Review file reading and writing, network access, commands, and connections with other tools separately.
- Prefer single permissions and limit access to essential resources.
- Check the result of actions and revoke persistent access when the workflow ends.
- Avoid sharing credentials or sensitive documents until you understand where they are processed and stored.
An agent’s capabilities depend on the tools and permissions it has, not on its label or ability to generate plans. In Android Studio, review the Gemini agent’s permissions for project files, domains, shell commands, and MCP servers, and configure the Agent Shell Sandbox if needed.