When the Cloud Comes into Play
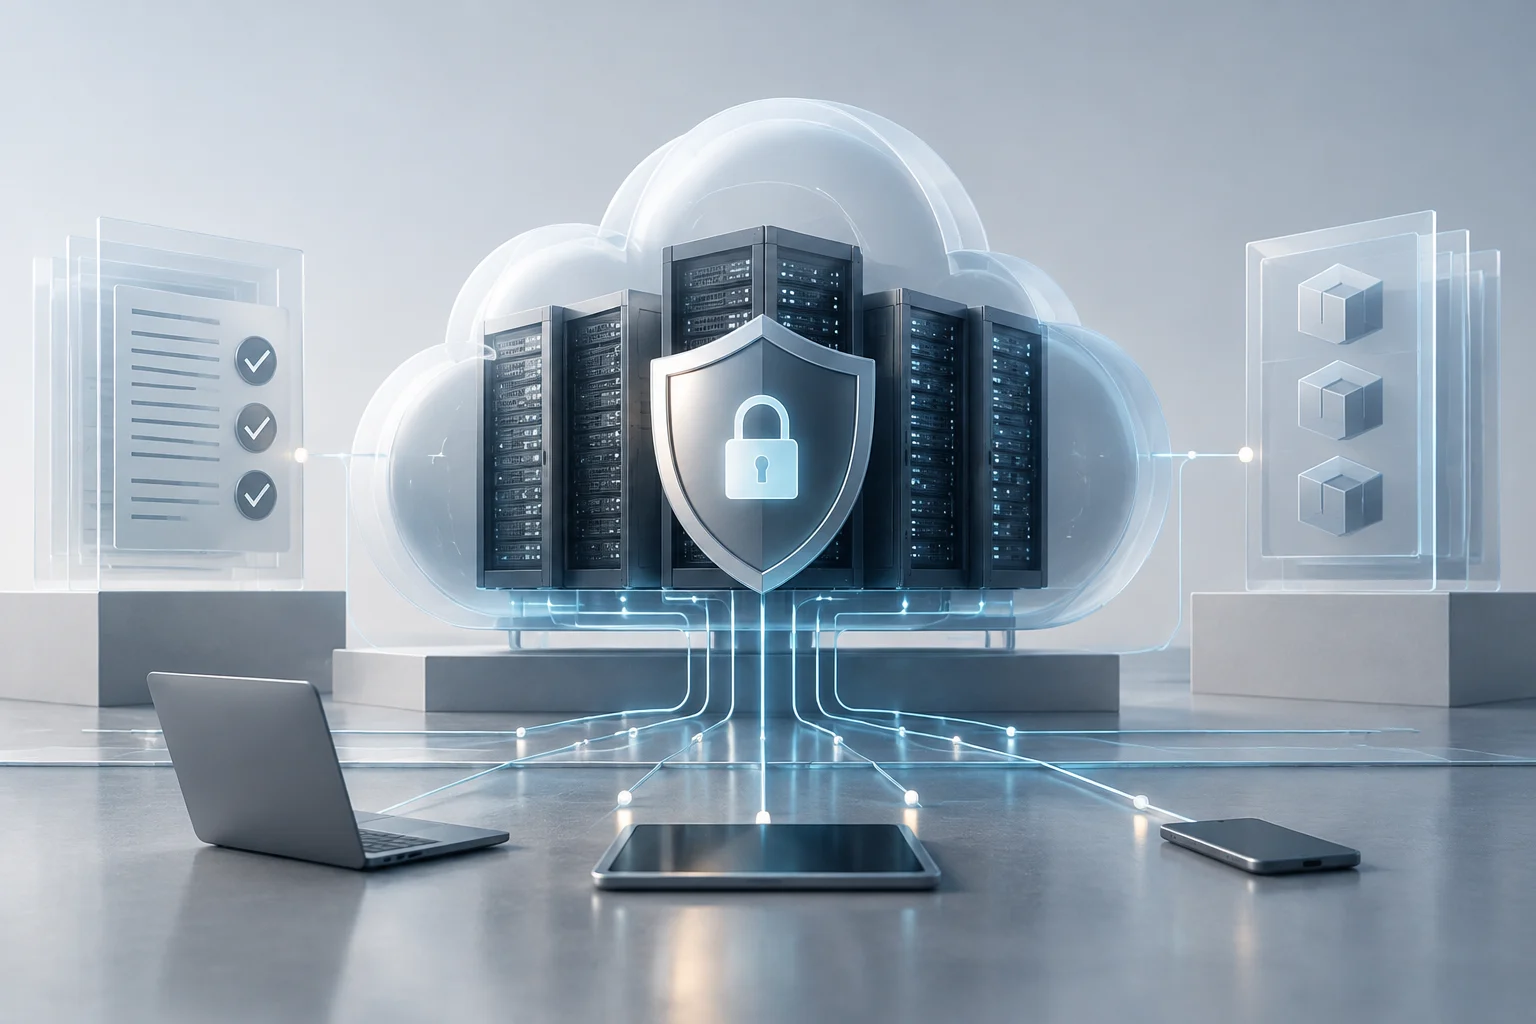
Apple presents on-device processing as a central part of data security and privacy. When an advanced Apple Intelligence request requires work with complex data and larger foundation models, the system may use Private Cloud Compute (PCC), the cloud service the company designed for those tasks.
In practical terms, the difference is where the request is processed: on the device when it can perform the task, or on PCC nodes when Apple Intelligence needs larger models. Apple says personal data sent to PCC is not accessible to the company itself. This is an assurance stated by Apple, supported, according to its explanation, by technical measures; it is not a promise that any system is invulnerable.
The Architecture Apple Describes
Apple describes PCC nodes as servers with custom silicon and hardware security technologies also used in iPhone, including Secure Enclave and Secure Boot. They run a hardened operating system based on iOS and macOS foundations and adapted to language-model inference workloads.
The architecture excludes general-purpose administration tools, such as remote shells and broad introspection mechanisms. Instead, Apple says it uses components intended to provide a limited set of operational metrics. The machine-learning stack was built with Swift on Server; the company attributes memory safety to the inference-control and dispatch layers written in Swift, together with isolation between address spaces.
The request must be available to the node that performs inference: Apple explains that end-to-end encryption cannot prevent that node from accessing the data needed to respond. Its design aims to encrypt the request from the device to validated PCC nodes, so components outside that trust boundary cannot decrypt it.
What Happens to Request Data
Apple defines PCC as a stateless processing system for personal data. According to the company, data is used exclusively to fulfill the request, remains on the nodes processing it until the response is returned, and is not retained afterward, including through logging or debugging.
The company also describes mechanisms intended to reduce the possibility that data persists. Secure Enclave randomizes the encryption keys for the data volume at every reboot, so data written there cannot be retained after that reboot. In addition, the inference process deletes data associated with a request when it is completed and periodically recycles the address spaces that handle it.
These measures explain the design Apple attributes to the service; they should be distinguished from a zero-risk guarantee. The documentation describes controls intended to limit access, retention, and exposure, not a claim that data can never be affected by a vulnerability.
Transparency and Research Tools
Apple says it publishes PCC software measurements in a cryptographically protected transparency log and makes production-version images available for inspection. According to the company, devices send requests only to nodes that can attest to running software publicly included in that log. This makes it possible to compare the inspected software with what Apple says is running in production.
The Virtual Research Environment (VRE) allows researchers to study PCC from a Mac with Apple silicon. Apple says it runs node software in a virtual machine with minor modifications and includes a virtual Secure Enclave Processor. Possible tasks include examining releases, checking log consistency, launching a virtualized release, and running inference with demonstration models.
Apple’s research announcement placed the VRE in the macOS Sequoia 15.1 preview available when that announcement was published and specified hardware requirements. That reference is time-bound: by itself, it does not establish current availability. The company also offers source code for certain PCC components, such as CloudAttestation and Thimble, under a limited-use license.
Reducing the Possibility of Targeted Attacks
PCC’s design includes a property Apple calls target diffusion: the aim is to prevent an attacker from directing a particular person’s requests to selected nodes based on identity or content. To achieve this, metadata visible outside the trust boundary excludes personally identifiable information and includes only limited context needed for routing.
Apple also explains that requests pass through an OHTTP relay operated by a third party, which hides the originating IP address before requests reach PCC infrastructure. The company says that, to direct traffic based on that IP address, an attacker would have to compromise both the relay and the load balancer. This specific effect does not mean the relay prevents every form of association or attack.
The system also uses one-time credentials based on blind RSA signatures to authorize requests without linking them to a specific person. Apple describes these measures as defenses that limit the ability to select users and reduce the impact of compromising a node, not as a guarantee that every targeted attack is impossible.
Rewards and Interpreting the Assurances
Apple has expanded its Apple Security Bounty program to include vulnerabilities that compromise PCC’s fundamental protections. In the company’s published table, the maximum reward of one million dollars applies to remote code execution with arbitrary privileges in the request-data attack category. Other types of flaws have different maximum amounts.
To interpret these assurances, it is useful to separate three things: the architecture Apple describes, the technical protections it says it has incorporated, and the ability of specialists to examine the software and report findings. The transparency log and VRE facilitate that research, but do not replace the assessment of each vulnerability or turn the manufacturer’s statements into a guarantee of zero risk.
In short, PCC is the cloud pathway Apple designed for certain advanced Apple Intelligence requests. The company says it limits data access and retention and provides resources to review its implementation; anyone assessing a specific request should bear in mind that the details here describe the system, not a list of features or terms of use for every device.