The Regulatory Framework and Its Scope in Spain
The Regulation (EU) 2024/1689, known as the AI Act, is a comprehensive regulatory framework for artificial intelligence. Unlike European directives, this text has direct application in all Member States without the need for national transposition. This means that Spanish companies must comply with its provisions from the dates established by the regulation itself, without waiting for a law from the Congress or the Senate.
The norm adopts a risk-based approach: the greater the potential impact of an AI system on individuals' fundamental rights, the stricter the obligations it imposes. This logic generates four risk levels that determine what each company must do depending on the system it uses or develops. The regulation distinguishes between providers, who develop or market the system, and deployers, who use it under their authority. Both figures have obligations, although of different intensity.
In Spain, supervision falls under the AESIA (Spanish Agency for the Supervision of Artificial Intelligence), created by Royal Decree 729/2023 with headquarters in A Coruña. This agency has the power to inspect systems, request documentation, impose corrective measures, and propose sanctions. The existence of an active national authority provides a dedicated body to oversee compliance with the regulation.
Application Timeline: What Is in Force and What Has Been Delayed
The application of the AI Act is phased. Prohibited practices and the AI literacy obligation (Article 4) have been in force since February 2, 2025. Obligations for general-purpose AI models (GPAI) and the sanction regime apply from August 2, 2025. The critical date for most companies is August 2, 2026, when the general application of the regulation enters into force, including the transparency obligations of Article 50.
However, the Digital Omnibus on AI (Regulation (EU) 2026/1744), in force since July 27, 2026, has modified the timeline for high-risk systems. Systems listed in Annex III (employment, education, essential services, biometrics) now have until December 2, 2027, to comply. High-risk systems integrated into products regulated by sectoral legislation (Annex I: machinery, medical devices, aviation) have a deadline until August 2, 2028. This modification does not delay the general application of transparency, prohibitions, or literacy, which maintain their original dates.
Key Dates of the AI Act
| Date | Obligation | Status |
|---|---|---|
| Feb 2, 2025 | Prohibitions and AI literacy | In force |
| Aug 2, 2025 | GPAI models and sanctions | In force |
| Aug 2, 2026 | Transparency (Art. 50) and general application | In force |
| Dec 2, 2027 | High-risk Annex III | Upcoming |
| Aug 2, 2028 | High-risk Annex I | Upcoming |
Transparency Obligations: Article 50
From August 2, 2026, Article 50 of the regulation requires that AI systems inform users when they interact with an artificial intelligence. Chatbots, virtual assistants, and interactive systems must clearly indicate that the user is dealing with a machine, not a person. This obligation applies to systems intended for direct interaction with humans.
Content generated or altered by AI, including deepfakes (images, videos, or audio edited or generated with AI), must be labeled as such. Furthermore, providers of generative systems must implement machine-readable marks in the synthetic output so that it can be automatically detected. This measure seeks to reduce deception and manipulation, and help people make informed decisions.
For Spanish SMEs using customer service chatbots, content generators, or AI marketing tools, compliance with these transparency rules is required. The European Commission has published a list of more than 180 organizations that have signed the Code of Good Practices on the transparency of AI-generated content, which offers a practical way to demonstrate compliance. Companies that do not implement these measures expose themselves to sanctions.
High-Risk Systems: Sectors and Requirements
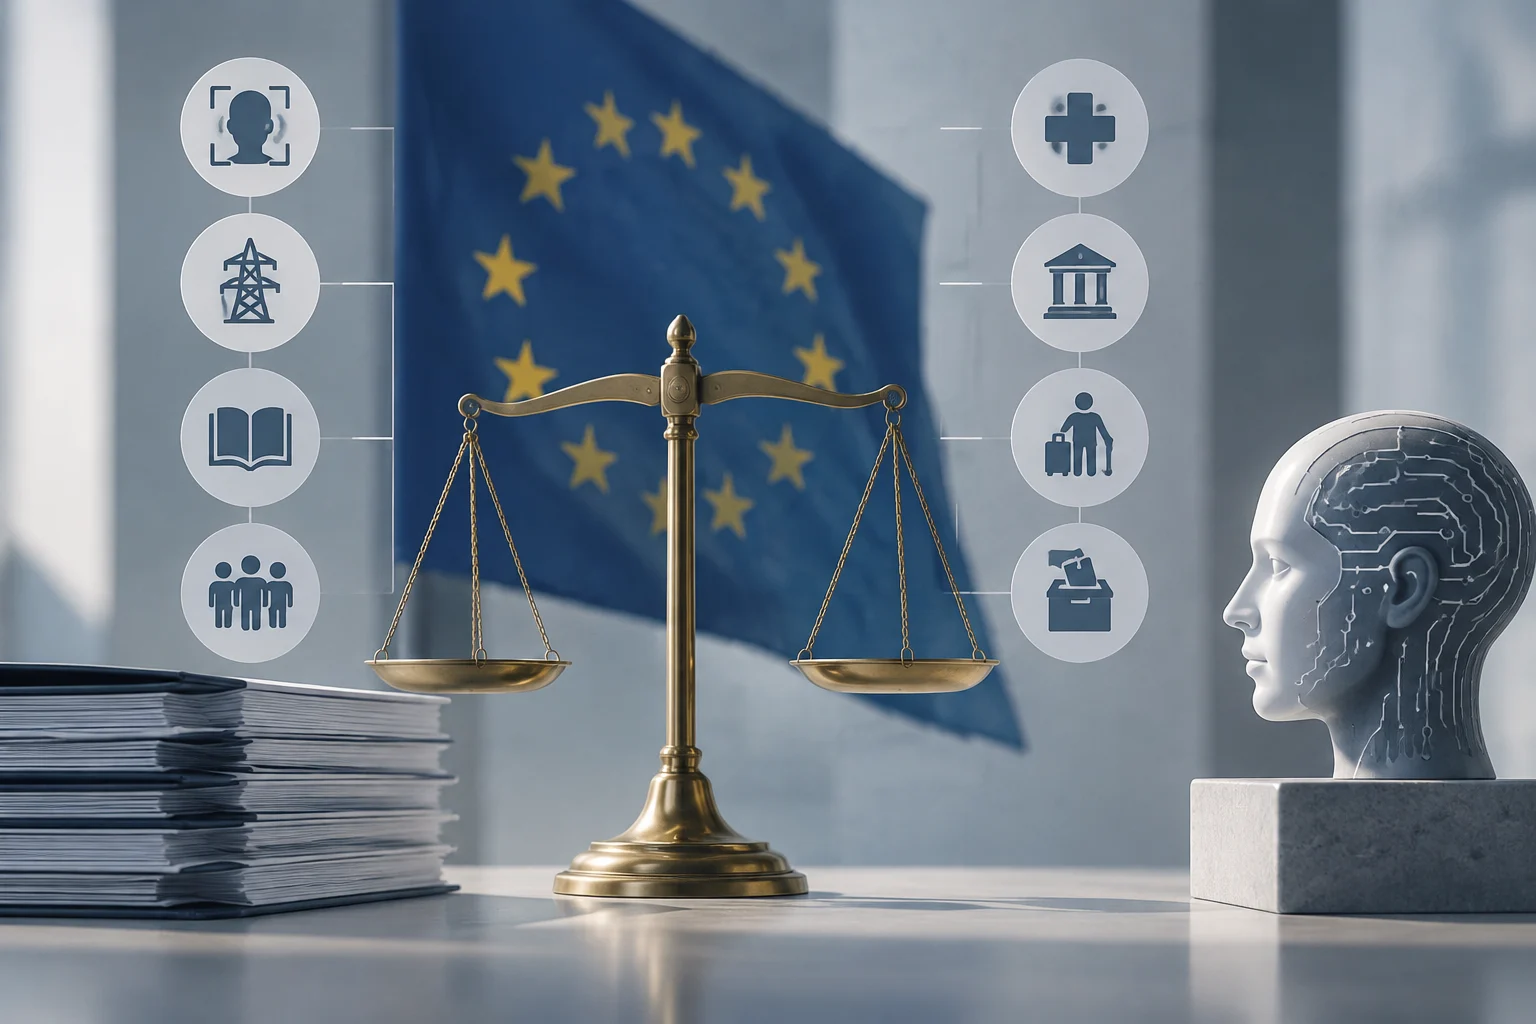
High-risk AI systems are those that can significantly affect the health, safety, or fundamental rights of individuals. Annex III of the regulation lists eight areas: biometrics, critical infrastructure, education, employment, access to essential services, law enforcement, migration, and administration of justice and democratic processes. If a company uses AI to filter resumes, evaluate candidates, determine promotions or dismissals, it is operating in the high-risk area.
These systems must meet strict requirements: continuous risk management, data governance, detailed technical documentation, activity logging, transparency in use, effective human oversight, and cybersecurity measures. Human oversight is not a formality: the system must be designed to allow a person to understand its functioning, monitor its behavior, interpret its results, and intervene or stop it when necessary.
The technical documentation must include a detailed description of the system, its purpose, performance metrics, training data, and test results. Activity logs must allow the traceability of the system's decisions and facilitate subsequent supervision. For companies that develop or deploy these systems, preparation must begin now, although the deadline for Annex III systems is December 2027, to avoid rushed and deficient compliance.
Sanctions and Penalty Regime
The AI Act's sanction regime is severe. Non-compliance with prohibited practices (unacceptable risk) can result in fines of up to 35 million euros or 7% of global annual turnover, whichever is higher. For SMEs and startups, fines are calculated proportionally, applying the lower amount between the fixed figure and the percentage of turnover.
Non-compliance with obligations for high-risk systems (human oversight, documentation, risk management) can result in fines of up to 15 million euros or 3% of global turnover. Incorrect information to authorities can cost up to 7.5 million euros or 1% of turnover. These amounts are designed to be deterrent even for large companies, and for SMEs represent a significant financial risk.
The AESIA participates in the supervision of compliance in Spain. The agency can inspect systems, request documentation, impose corrective measures, and propose sanctions before the courts. Advance preparation allows companies to better manage their obligations and reduce the risk of non-compliance when supervision intensifies.
Practical Roadmap for Compliance
The first step is to carry out an inventory of AI systems that the company uses, develops, or deploys. This includes third-party tools such as ChatGPT, Copilot, AI HR tools, intelligent CRMs, and content generators. Each system must be identified with its provider, purpose, and risk level.
The second step is the risk classification of each system according to the regulation's classification. High-risk systems require the most demanding measures, while limited-risk systems mainly need transparency. The AI literacy obligation (Article 4) applies to staff who work with AI systems, requiring providers and deployers to take measures to ensure a sufficient level of AI literacy.
Key Steps for Compliance
- Inventory: Identify all AI systems in use.
- Classification: Determine the risk level of each system.
- Training: Ensure staff literacy for those working with AI (mandatory since February 2025).
- Documentation: Establish technical and governance documentation for high-risk systems.
- Transparency: Implement AI interaction notices and labeling of generated content (mandatory since August 2026; generative systems already on the market have until December 2026 for machine-readable marking).
- Supervision: Assign effective human oversight to high-risk systems.
The documentation and governance are essential to demonstrate compliance, particularly for high-risk systems where technical records and activity logs are required. Team training helps ensure that staff can use AI tools safely and effectively. Early preparation allows companies to manage their obligations and reduce the risk of compliance gaps when supervision intensifies.