The Difference Between Installing and Verifying
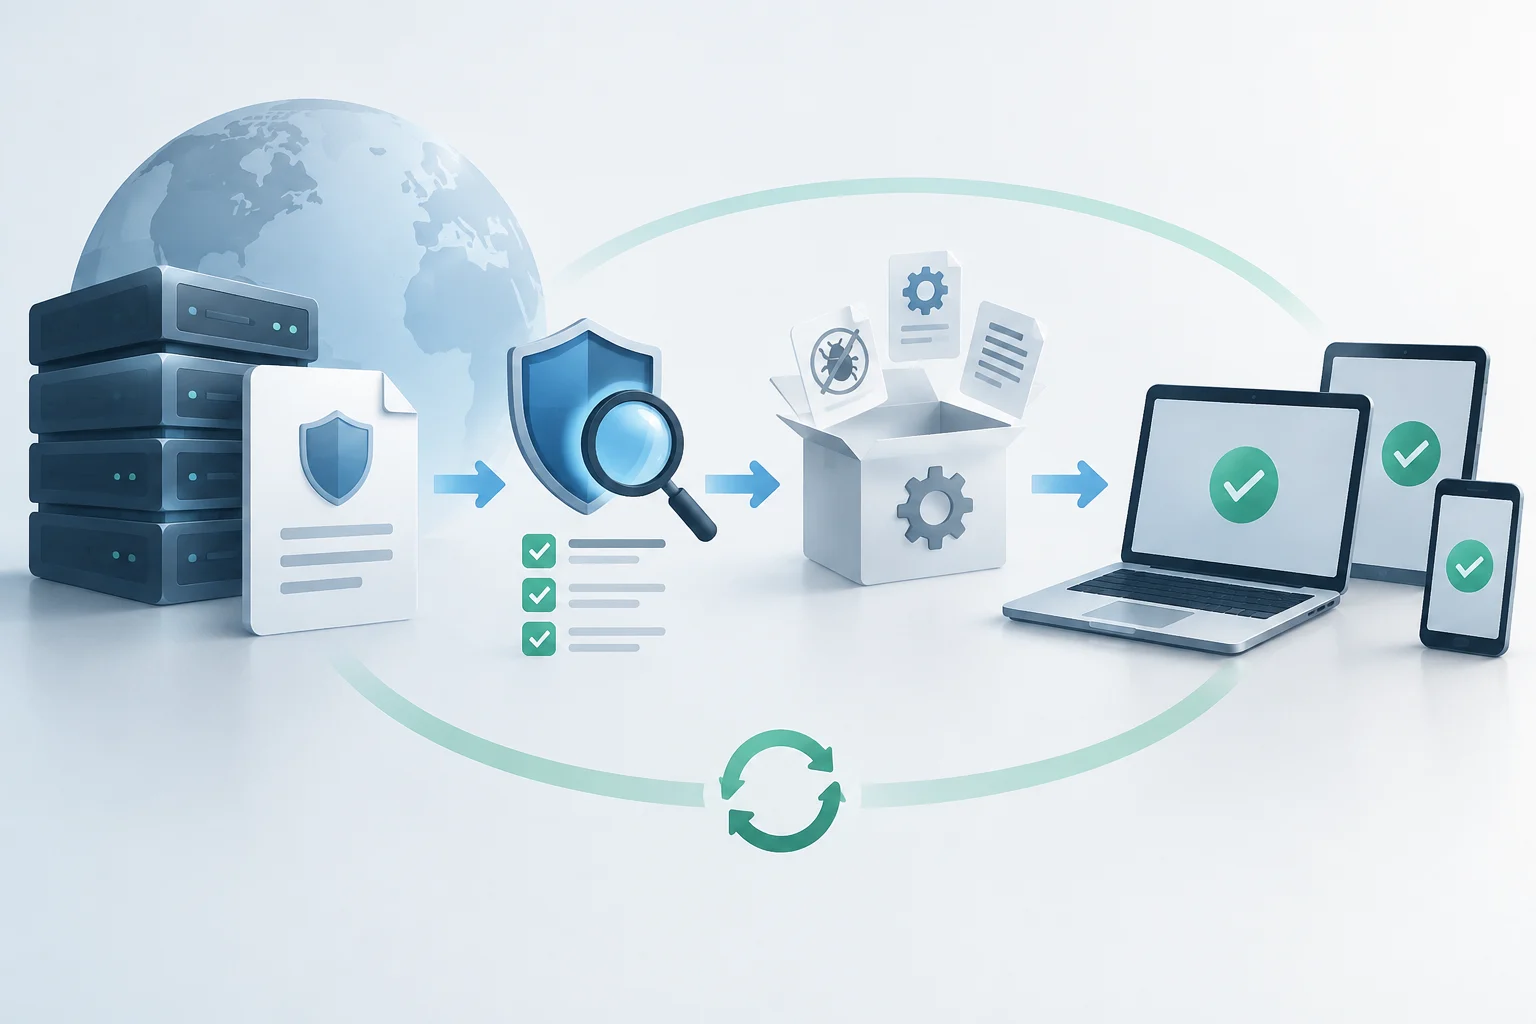
Installing an update does not automatically guarantee that a system is protected. Verifying authenticity is the critical step that distinguishes a legitimate patch from a download error or an attempt at spoofing. Many users assume that when the operating system displays a success message, the process has completed correctly. But that message does not validate the integrity of the files or the validity of the digital signature that backs them.
This guide focuses on the actual state of protection, not merely on the act of updating. Technical validation helps confirm that critical patches have been applied properly and that no known vulnerabilities remain unresolved. For home users and professionals managing their own devices, this distinction is essential to avoid false assurances about security.
An operating system’s success message indicates that installation has finished, but it does not certify that the content is intact. Integrity depends on files remaining unaltered during transfer or storage. Without an explicit check, users face the possibility that a critical component was not applied correctly, leaving a latent security gap that is not visible in the user interface.
Windows 11: Status and Digital Signatures
In Windows 11, the Windows Security app is the starting point for checking update status. From the “Device security” section, users can access detailed information about Secure Boot and certificate status. As of April 2026, the app displays colored indicators—green, yellow or red—to show whether the device has received the necessary Secure Boot certificate updates, which expire in 2026.
Command-line tools can be used to validate the digital signature of installed patches. The signtool verify command checks the certificate chain for a specific file. Although Microsoft does not provide a direct graphical interface to validate each individual Windows Update patch, system integrity is checked through Secure Boot status and the integrity of system files. If a patch fails, the system marks it as pending or failed; that status should be investigated immediately.
Secure Boot is a fundamental barrier that prevents unsigned code from running during startup. The chain of trust begins with the firmware and continues through the operating system, ensuring that each stage is validated by the manufacturer. If Secure Boot certificates are out of date, the system may display warnings or, in extreme cases, refuse to start. This underscores the importance of keeping these components current.
Android: Google Play System Updates
On Android devices, verification is performed through the Google Play System Updates feature. It lets users check the current Google Play system version and find out whether security updates are pending. The process is straightforward: go to Settings > Security & privacy > System & updates to prompt a search for new versions. If an update is available, the system downloads and installs it; a restart is often required to complete the process.
It is important to distinguish the Android version from the Android security update. The former refers to the platform level, while the latter indicates the date of the most recent security patch applied. Both details are visible under “About phone.” If the security update date is old, the device may be exposed to known vulnerabilities, regardless of which Android version is installed.
Keeping the platform version separate from the security patch allows manufacturers to release critical fixes without updating the entire user interface. The patch date is the most reliable indicator of a device’s current protection. A device running a recent Android version but an old security patch remains vulnerable to exploits fixed in earlier platform releases.
Warning Signs and Spoofing
Spotting a failed update or a spoofing attempt requires attention to detail. Failed updates usually leave a trace in Windows Update history or Android event logs. In Windows, if a critical patch does not install, the system lists it as “Pending” or “Error.” On Android, if Google Play System Updates cannot complete an installation, the cause may be a lack of storage space or a network error.
Attempts to spoof updates are rare but possible. Digital signature validation is the only way to confirm that code comes from the legitimate manufacturer. In Windows, driver and patch files must be signed by Microsoft. On Android, system updates are signed by Google or the device manufacturer. Any signature discrepancy should be treated as a critical warning sign.
Repeated installation errors can indicate a software conflict or an underlying hardware problem. Log analysis helps distinguish a temporary network failure from a structural problem in the system. Ignoring these errors can lead to a buildup of unpatched vulnerabilities, increasing the risk of exploitation by malicious actors.
Advanced Diagnostic Tools
For advanced users, command-line tools provide a higher level of detail. In Windows, the wmic qfe list command lists all installed security updates, showing their KB ID and installation date. This is useful for checking whether a specific patch has been applied correctly. On Android, the adb shell getprop command can retrieve detailed information about the system version and the security patches applied.
These tools make it possible to audit update history and detect recurring failure patterns. If a patch installs and is later removed, or if errors keep recurring, advanced diagnostics can help identify the root cause. In corporate environments, tools such as Ivanti or IBM MaaS360 can manage and verify update status across device fleets, helping ensure that all equipment complies with security policies.
The ability to extract raw system data provides an independent way to verify graphical reports. Traceability for every patch is essential for meeting strict security requirements. In business environments, automating these checks with scripts or fleet-management tools reduces operational workload and minimizes the risk of human error.
A Monthly Verification Routine
Maintaining device security requires a consistent routine. Monthly verification should include checking update status in Windows Update and Google Play System Updates. In Windows, review “Update history” to confirm that the previous month’s critical patches are installed. On Android, check the date of the latest security update under “About phone.”
It is also advisable to review Secure Boot status in Windows and the integrity of Google Play services on Android. If an anomaly is detected, such as a pending patch or a signature error, take action immediately. This routine not only protects against known vulnerabilities but also helps ensure that the operating system runs with maximum stability and performance.
Consistency in verification matters as much as installing patches. Operational discipline prevents security debt from accumulating on a device. By setting a regular schedule for these checks, users can keep their devices aligned with the latest available defenses and reduce the potential attack surface.