What is an Identity Management System (IAM) and how does it differ from a simple password manager?
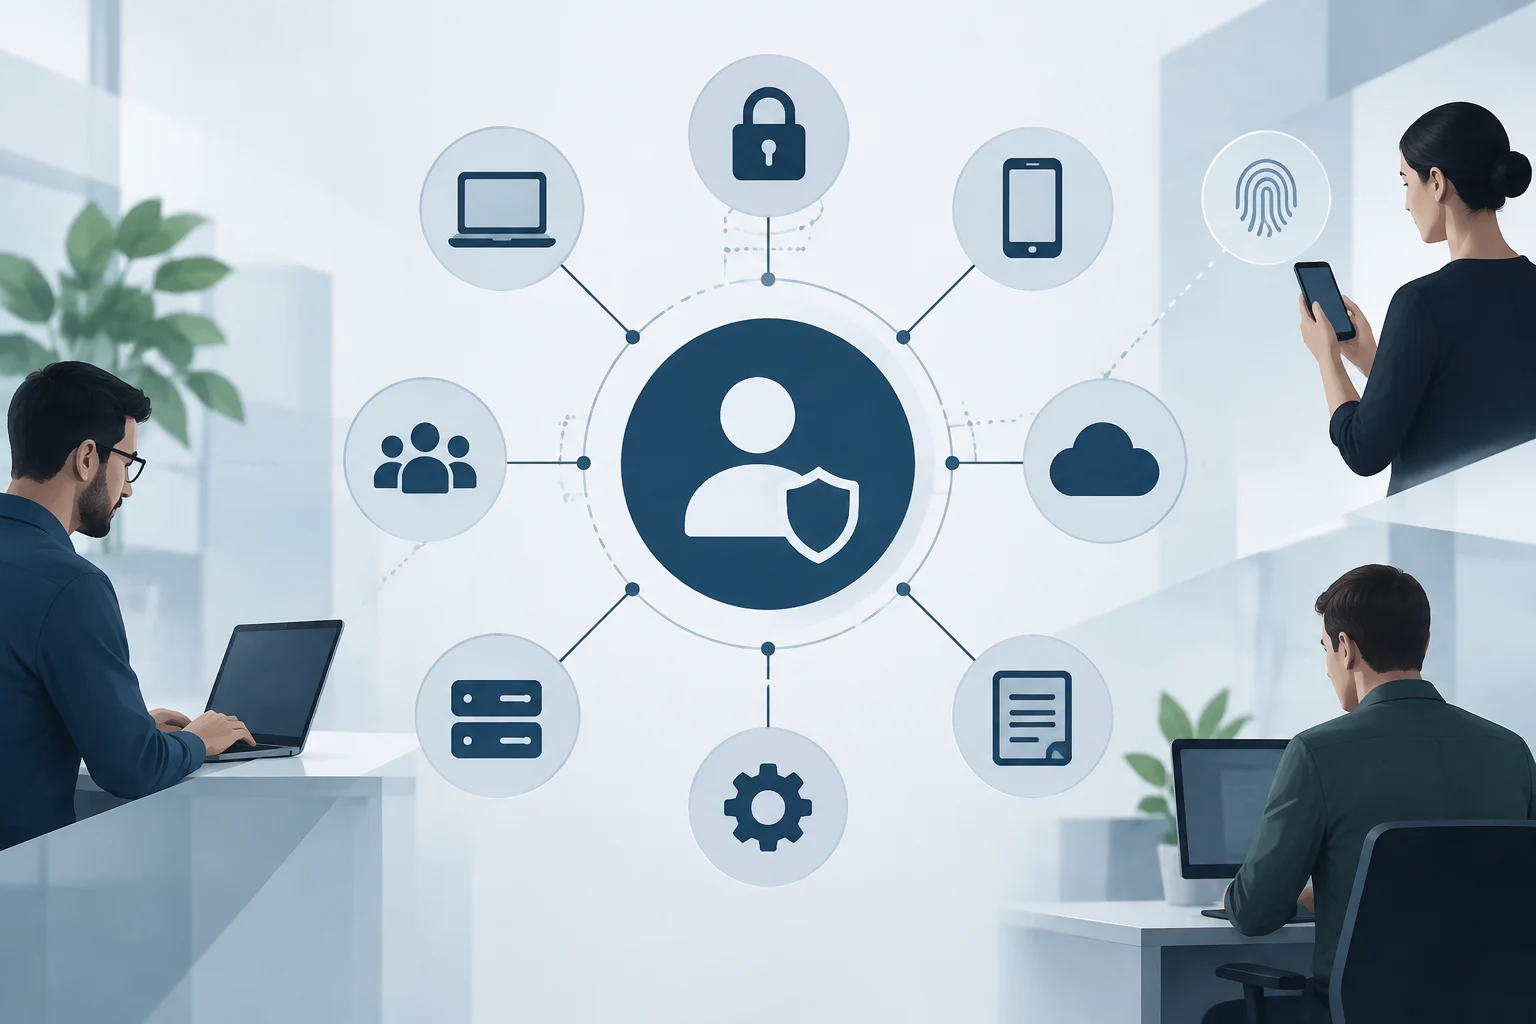
Identity and Access Management (IAM) is the cybersecurity discipline responsible for provisioning and protecting digital identities and user access permissions within an IT system. Unlike a password manager, which only stores credentials, an IAM system ensures that the right people access the right resources for the right reasons at the right time. This distinction is crucial because IAM covers the complete identity lifecycle, from creation to revocation, integrating security and audit policies.
With the rise of cloud computing, remote work, and generative AI, IAM has become a central component of network security. Modern corporate networks host an increasing number of human and non-human users, such as AI agents, IoT devices, and automated workloads. According to the IBM X-Force Threat Intelligence Index, 30% of cyberattacks involve the theft and abuse of valid accounts, highlighting the need for robust identity management beyond simple password authentication.
Which standard protocols (SAML, OIDC, SCIM) should the software support to ensure interoperability?
The choice of authentication protocol determines the ease of integration and the adaptability of the solution to different environments. SAML 2.0, an OASIS standard from 2005, was designed for XML-based identity federation in traditional enterprise environments. On the other hand, OpenID Connect (OIDC), launched in 2014 by the OpenID Foundation, extends OAuth 2.0 with a lightweight JSON authentication layer, optimized for APIs, mobile applications, and modern web architectures. A modern Identity Provider (IdP) must support both protocols to facilitate integration with legacy and modern applications simultaneously.
In addition to authentication, it is fundamental to consider SCIM (System for Cross-domain Identity Management), which answers whether a user account exists and is up to date. While SAML and OIDC address authentication, SCIM manages the automated provisioning and deprovisioning of identities between systems. For an SME, requiring native support for these three protocols ensures that the IAM solution can scale and integrate with the cloud software ecosystem the company uses, avoiding identity silos and reducing the manual IT load.
How to evaluate the robustness of Multi-Factor Authentication (MFA) and account recovery options?
Multi-Factor Authentication (MFA) is an essential security layer that adds additional verification methods, such as biometrics, physical tokens, or authentication apps, in addition to the password. When evaluating an IAM solution, it is critical to verify that MFA is configurable based on risk and offers secure account recovery options. A system that is too rigid can frustrate users, while one that is too lax leaves security gaps. Access recovery is a critical area often ignored but vital to avoid operational lockouts in case of device or credential loss.
Best practices indicate that an effective IAM system must start with a solid foundation that includes clear account organization and the use of MFA to add protection. It is important that the provider offers recovery mechanisms that do not rely exclusively on a single factor, such as SMS, which can be intercepted. The evaluation should include stress tests on recovery flows to ensure that IT administrators can restore access quickly and securely without compromising system integrity.
What usability and technical support criteria are decisive for small IT teams?
In SMEs, IT teams are usually small, so the usability of the administration console and ease of integration are decisive factors. A complex IAM solution can become an operational burden that outweighs security benefits. It is essential that the interface allows intuitive management of roles, permissions, and access policies, minimizing the learning curve. Additionally, clear documentation and responsive technical support are vital for resolving incidents without relying on expensive external consultants.
The automation of processes such as credential onboarding, modification, and offboarding is another key criterion. Modern IAM systems allow automating these tasks, reducing the risk of human errors and freeing up time for higher-value tasks. When selecting a solution, one must evaluate whether the platform offers pre-configured templates for common cloud applications, which accelerates implementation. Usability is not just a matter of comfort, but of operational efficiency and risk reduction in resource-constrained environments.
How to verify the provider's security and compliance with data protection regulations?
The security of the IAM provider itself is as important as the security it offers to its clients. It is fundamental to verify that the provider complies with relevant data protection regulations, such as GDPR in Europe, and holds recognized security certifications. This includes encryption of data in transit and at rest, as well as secure development practices. A provider that does not prioritize the security of its own infrastructure can become a weak point in the SME's security supply chain.
Furthermore, it is recommended to request security audit reports and verify the provider's transparency in vulnerability management. Regulatory compliance is not just a legal requirement, but a guarantee that the provider follows industry standards in protecting sensitive data. When evaluating provider security, one must also consider its ability to offer regular security updates and its commitment to continuous improvement in cybersecurity practices.